Stop Hunting Advisories.
Start Fixing Incidents.
The First Purpose-Built Security Platform for PSIRT
Track CVE impact, manage advisories, and publish disclosures from a single platform. DefectDojo's PSIRT Advisory Engine eliminates the manual triage and guesswork of legacy PSIRT workflows.
PSIRT Teams Have Been Tasked with the Impossible
Advisory feeds never sleep. Spreadsheets don't scale. And the regulators are done waiting.
Security advisories are published around the clock from dozens of sources: CISA, NVD, RedHat, Exploit-DB, vendor RSS feeds, and more. For the specialized teams responsible for answering one question, "Are we impacted?", keeping up means checking feeds every morning, maintaining spreadsheets with thousands of rows, and spending 30 to 60 minutes manually analyzing each advisory.
Meanwhile, the pressure is only growing. Regulations including the EU Cyber Resilience Act (CRA), FDA cybersecurity guidance for medical devices, ISO 21434 for automotive, and NIS2 now mandate PSIRT capabilities across industries that never required them before. More than 10,000 organizations are projected to need formal PSIRT infrastructure by 2028.
Product security incident response deserves better than RSS readers and spreadsheets. It deserves the same automation that transformed the rest of AppSec.
PSIRT and AppSec, Finally on the Same Platform
DefectDojo is the open-source unified vulnerability management platform. The PSIRT Advisory Engine extends that foundation to product security incident response.
One Security System of Action
Your AppSec program already aggregates findings from 500+ security tools into a single system of action. Validated advisories flow directly into existing engagements and findings workflows, with status sync and tracking already in place. PSIRT stops being a silo and becomes part of your unified security posture.
Built for Compliance and Audit Readiness
SLA enforcement, full audit trails, and structured disclosure workflows help you meet the PSIRT requirements of the EU Cyber Resilience Act, FDA guidance, ISO 21434, and NIS2.
Automation That Scales
The same security automation that deduplicates, enriches, and prioritizes scanner findings now handles advisory triage, so a small PSIRT team can cover an entire product portfolio.
Born from Practitioners
DefectDojo was built by security engineers who lived these workflows. The PSIRT Advisory Engine was designed for the teams doing this work today, not a generic ticketing layer with a security label.
Why DefectDojo for PSIRT
One Security System of Action
Your AppSec program already aggregates findings from 500+ security tools into a single system of action. Validated advisories flow directly into existing engagements and findings workflows, with status sync and tracking already in place. PSIRT stops being a silo and becomes part of your unified security posture.
Built for Compliance and Audit Readiness
SLA enforcement, full audit trails, and structured disclosure workflows help you meet the PSIRT requirements of the EU Cyber Resilience Act, FDA guidance, ISO 21434, and NIS2.
Automation That Scales
The same security automation that deduplicates, enriches, and prioritizes scanner findings now handles advisory triage, so a small PSIRT team can cover an entire product portfolio.
Born from Practitioners
DefectDojo was built by security engineers who lived these workflows. The PSIRT Advisory Engine was designed for the teams doing this work today, not a generic ticketing layer with a security label.
How PSIRT Works in DefectDojo
From feed to disclosure, here's what product security incident response looks like when it runs inside DefectDojo.
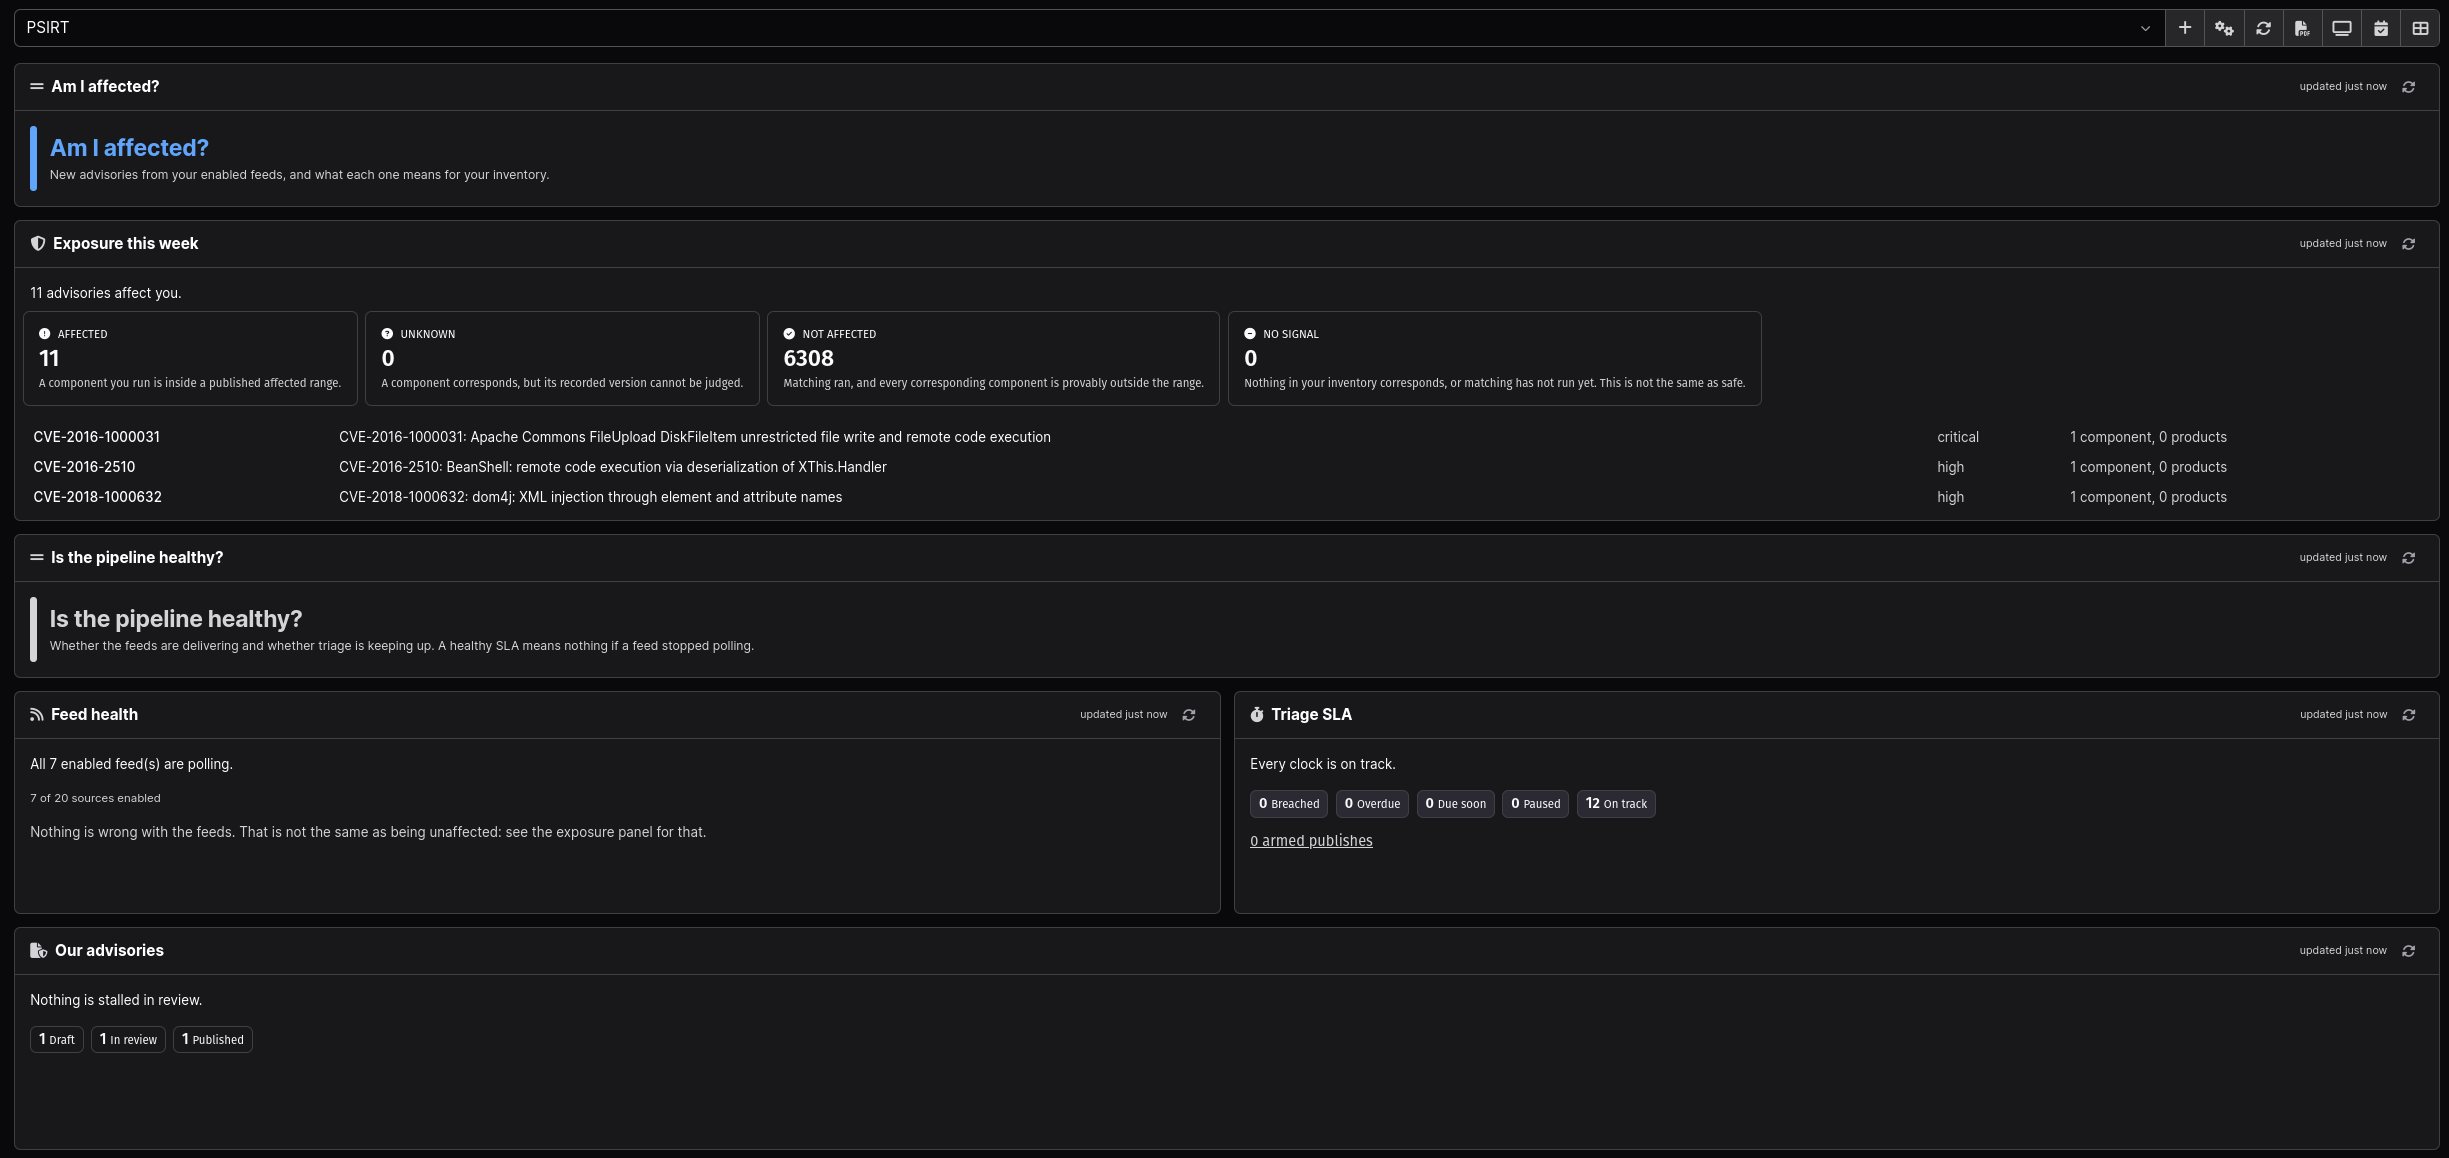
Connect Your Advisory Feeds
Point the PSIRT Advisory Engine at the sources your team already monitors. Advisories flow in automatically from CISA, NVD, EUVD, RedHat Security, Exploit-DB, and more than a dozen other feeds via RSS, API, and KEV. No morning feed checks. No copy-paste.
Match Advisories to Your Products
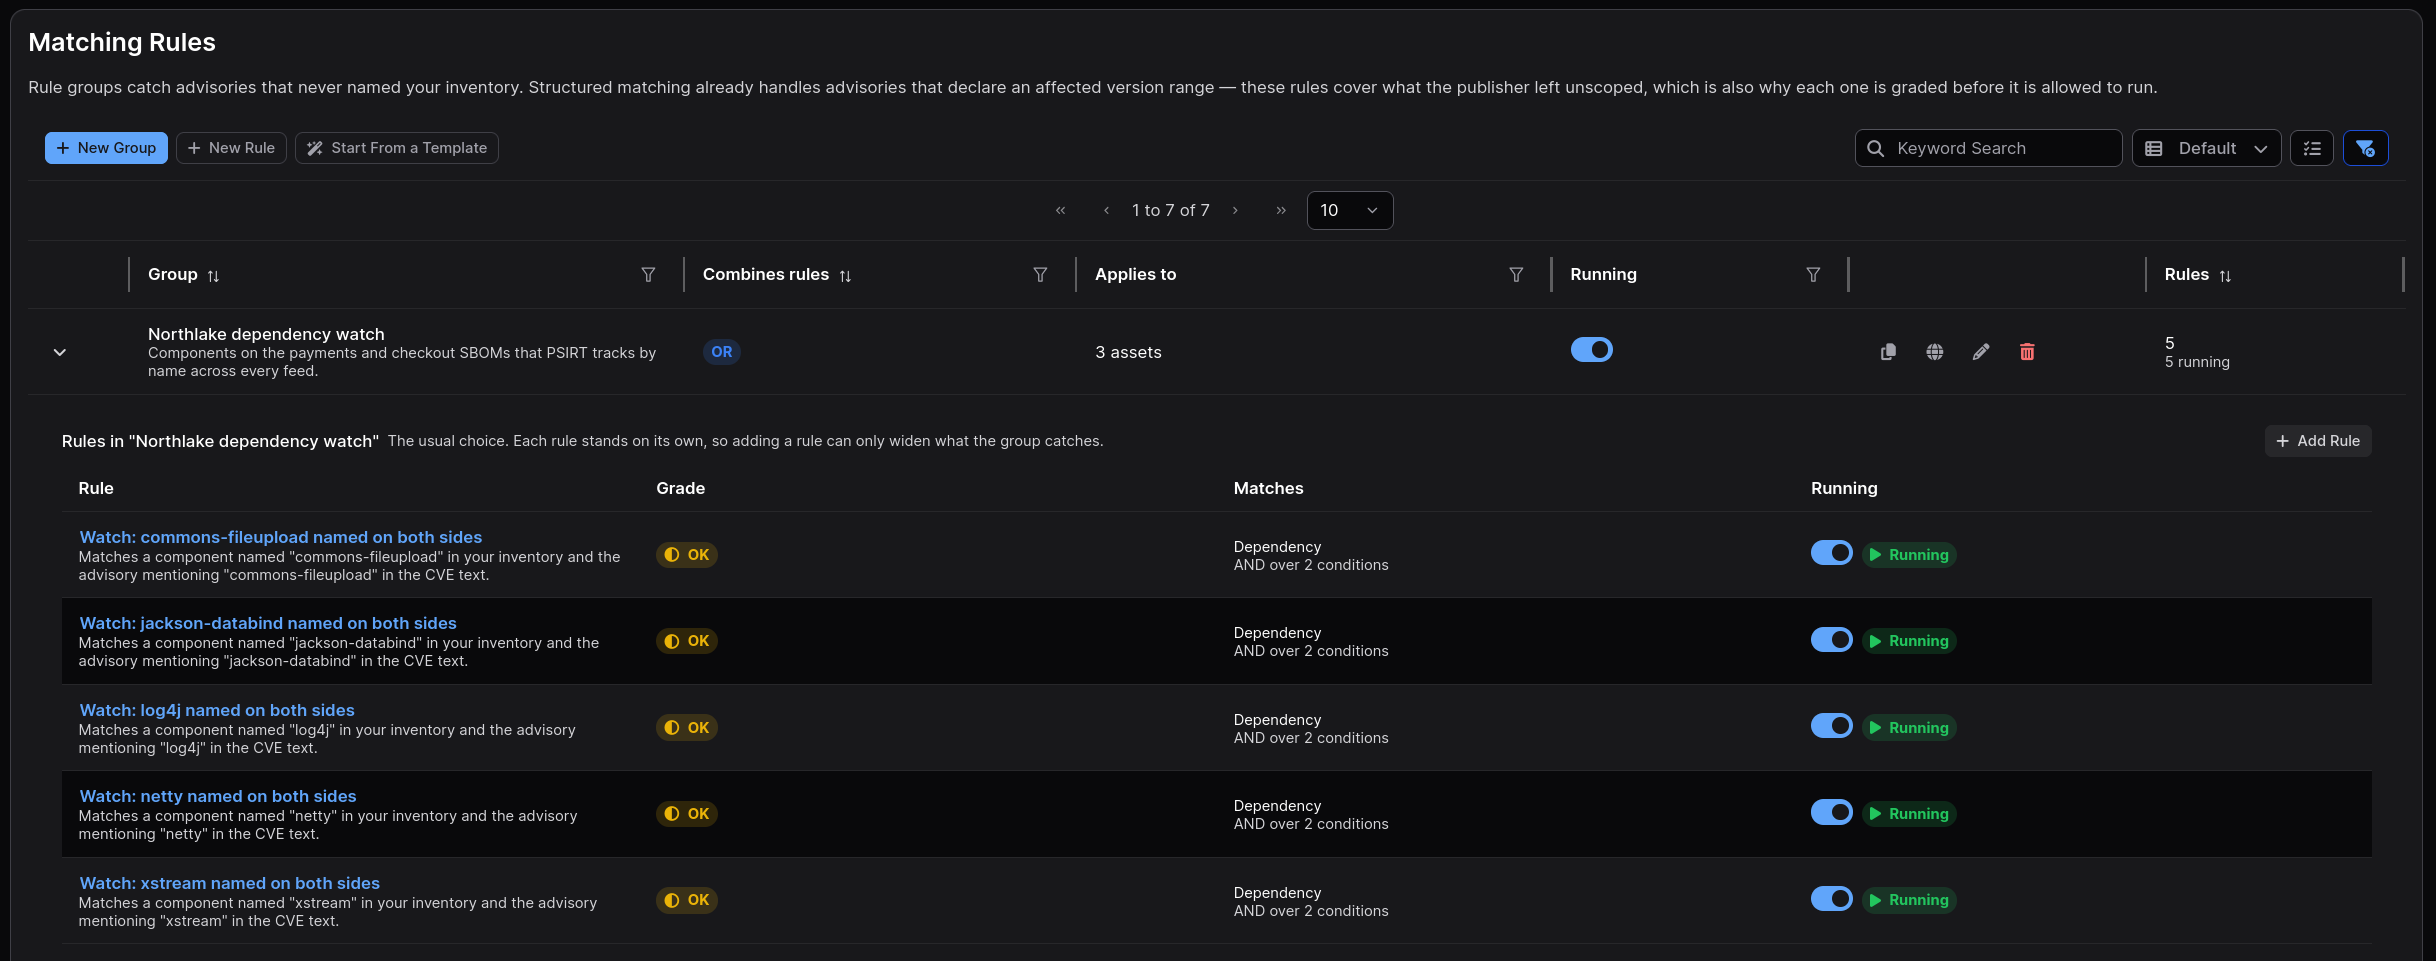
The engine cross-references every incoming advisory against your SBOM data in Locations, DefectDojo's component-level asset model, or against custom asset matching rules you define. Instead of manually checking whether a CVE touches any dependency across dozens of repos, you see exactly which products are impacted the moment an advisory lands.
Work a Prioritized Queue
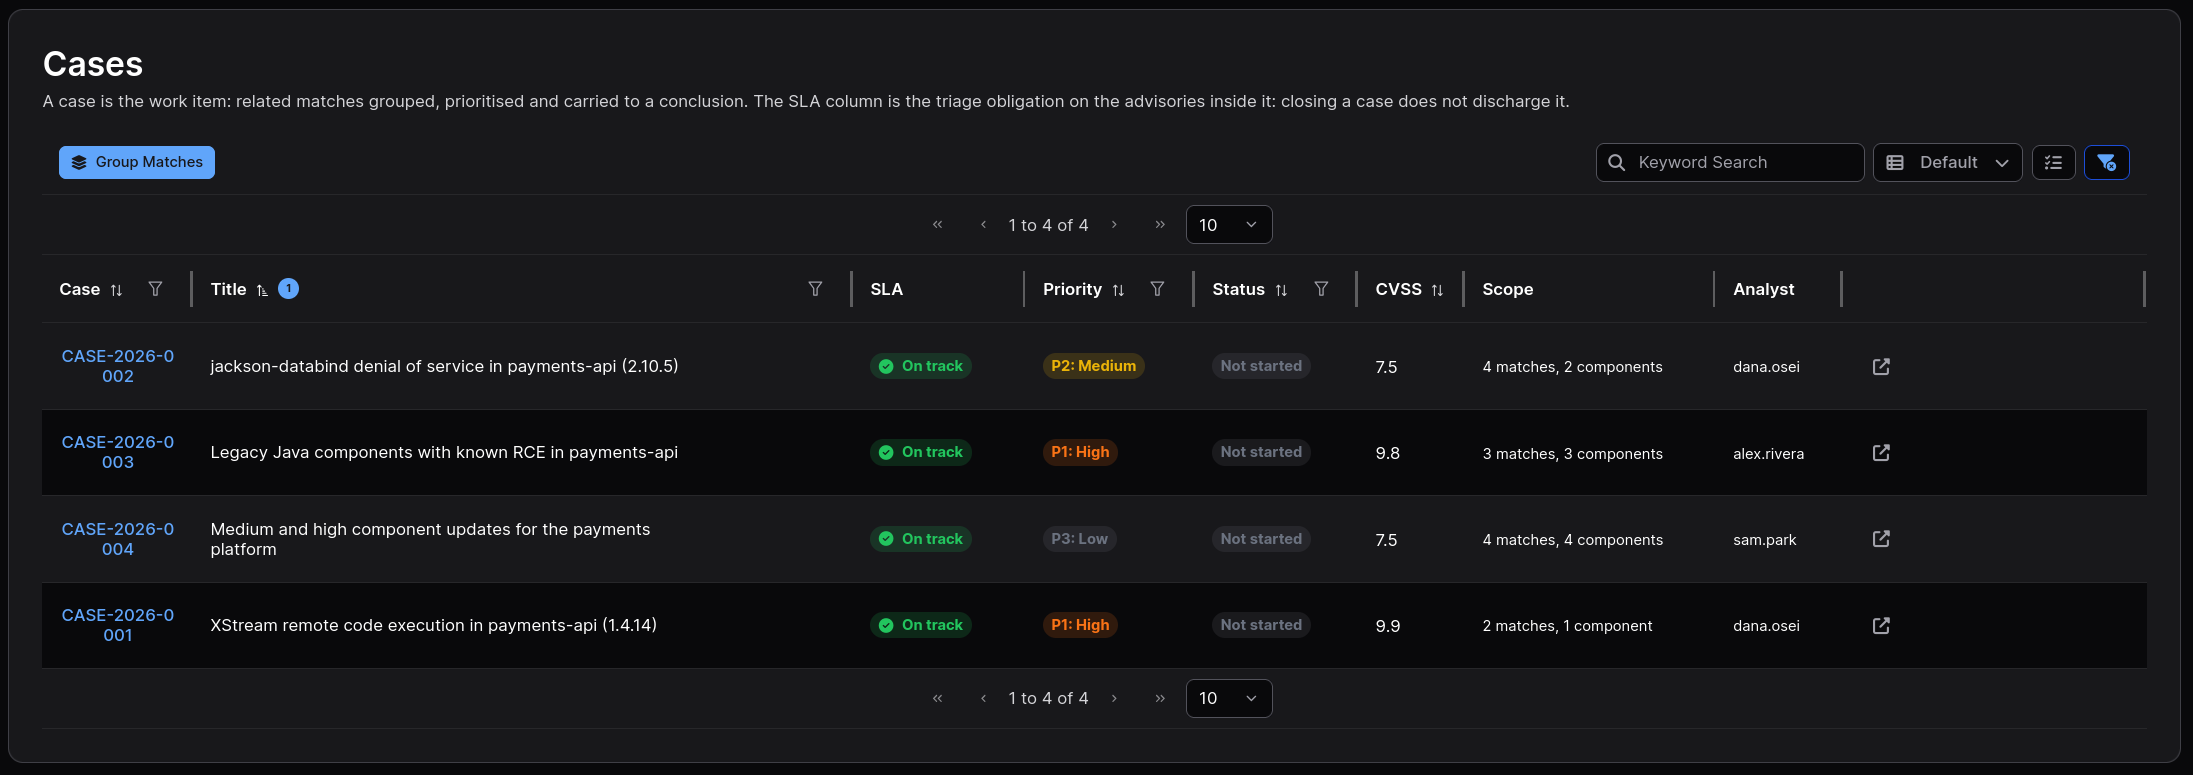
Matched advisories are scored using CVSS, EPSS, KEV status, and your own custom rules, then grouped into structured cases with clear ownership. Your PSIRT team opens one queue, ranked by real risk, and assigns advisories the way an AppSec team assigns findings.
Push Validated Advisories into DefectDojo Pro
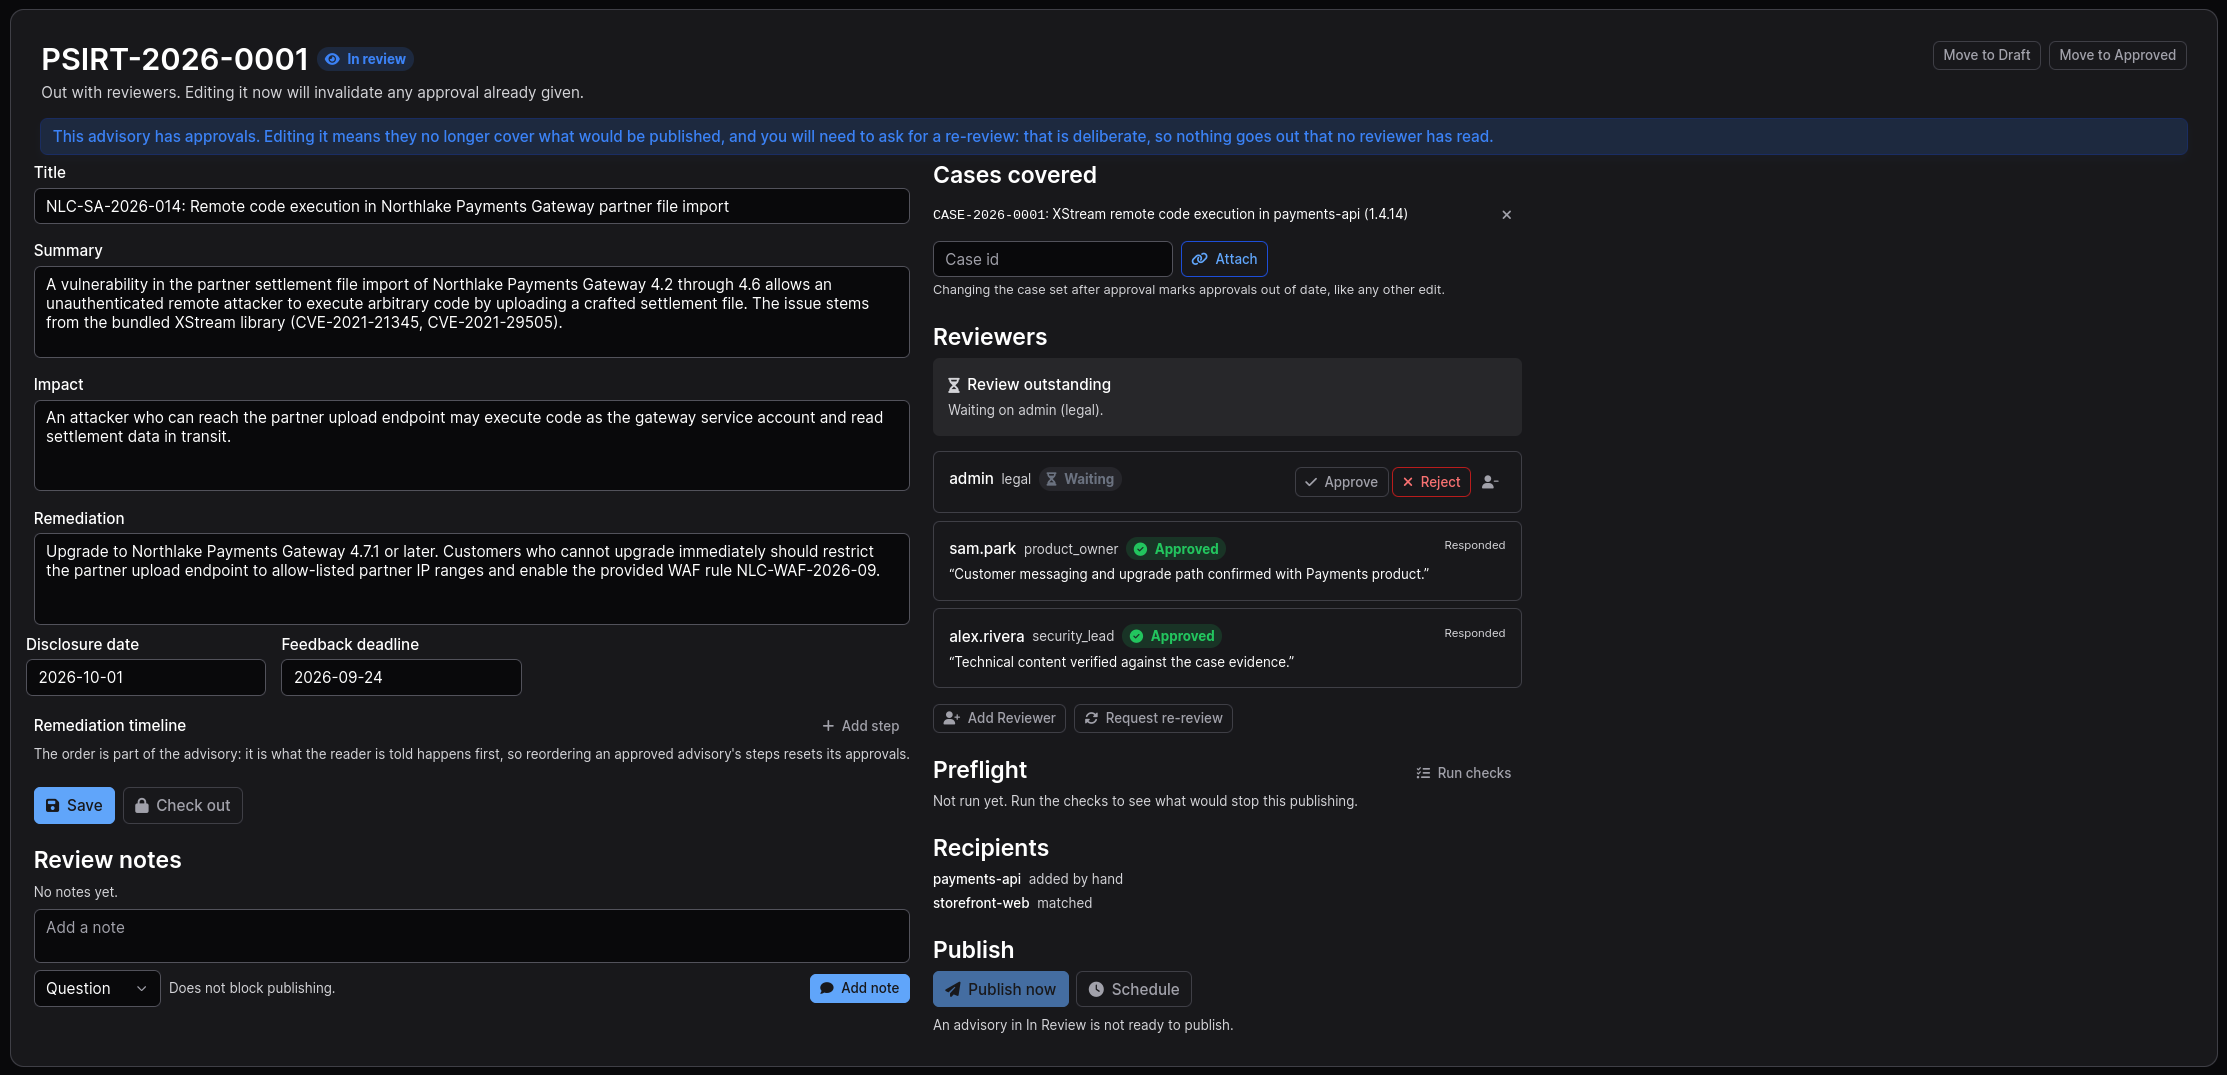
When an advisory is confirmed as relevant, push it directly into DefectDojo. It lands in your existing engagements and findings workflows with status sync in place, so remediation runs through the same security pipeline, ownership model, and SLAs as the rest of your vulnerability management program.
Publish and Track to Closure
Generate branded, professional PDF security advisories for customers and stakeholders directly from the platform. Then track remediation to closure with SLA enforcement and full audit data, giving you a defensible record for regulators and customers alike.
Frequently asked questions
What is a PSIRT?
A Product Security Incident Response Team (PSIRT) identifies, assesses, prioritizes, and responds to security vulnerabilities affecting an organization's products and services. Unlike a CSIRT, which protects internal infrastructure, a PSIRT focuses on the security of the products a company builds and ships to customers.
What is the PSIRT Advisory Engine?
The PSIRT Advisory Engine is DefectDojo's purpose-built capability for product security incident response. It automatically ingests security advisories from 20+ feeds, matches them against your SBOM or asset rules, prioritizes them by risk, and lets your team publish branded disclosures and track remediation inside DefectDojo Pro.
How does DefectDojo help with PSIRT compliance requirements?
Regulations including the EU Cyber Resilience Act, FDA cybersecurity guidance, ISO 21434, and NIS2 mandate formal product security incident response capabilities. DefectDojo provides the SLA tracking, audit data, and structured advisory workflows these frameworks require.
Does the PSIRT Advisory Engine work with my existing AppSec program?
Yes. If you already run AppSec or vulnerability management on DefectDojo, adoption is a natural extension. Advisories flow directly into your existing engagements and findings workflows with status sync and tracking in place.
Is the PSIRT Advisory Engine part of Community Edition or DefectDojo Pro?
The PSIRT Advisory Engine is a DefectDojo Pro capability, available in the cloud or self-hosted alongside your DefectDojo deployment.