Detection Was Never the Hard Part
Cloud Security Posture Management (CSPM) with DefectDojo.
Most CSPM tools stop at the dashboard. DefectDojo connects your AWS accounts, Azure subscriptions, and GCP projects, scans them for misconfigurations, and fixes what it finds: an infrastructure as code pull request, or a reversible change applied directly to the live resource. Your cloud security findings live beside every other security finding, in one system of action.
Cloud Security Has a Follow-Through Problem
Every CSPM tool on the market can find a public S3 bucket. Finding it was never the hard part. The hard part is what happens next: the misconfiguration gets exported to a spreadsheet, re-keyed into a ticket, routed to a cloud operations team that is already underwater, and rediscovered by the next scan before anyone touched it.
Meanwhile, cloud security lives in one console and application security lives in another, so nobody can answer the only question that matters: what is our actual security posture, and is it getting better?
DefectDojo treats a cloud misconfiguration the way it treats every other security finding. It gets scanned, imported, deduplicated, prioritized, assigned, and fixed inside the same platform your team already uses for application security. And with Sensei, the fix itself happens without leaving DefectDojo.
CSPM Capabilities Built by Practitioners, for Practitioners
Multi-Cloud Onboarding
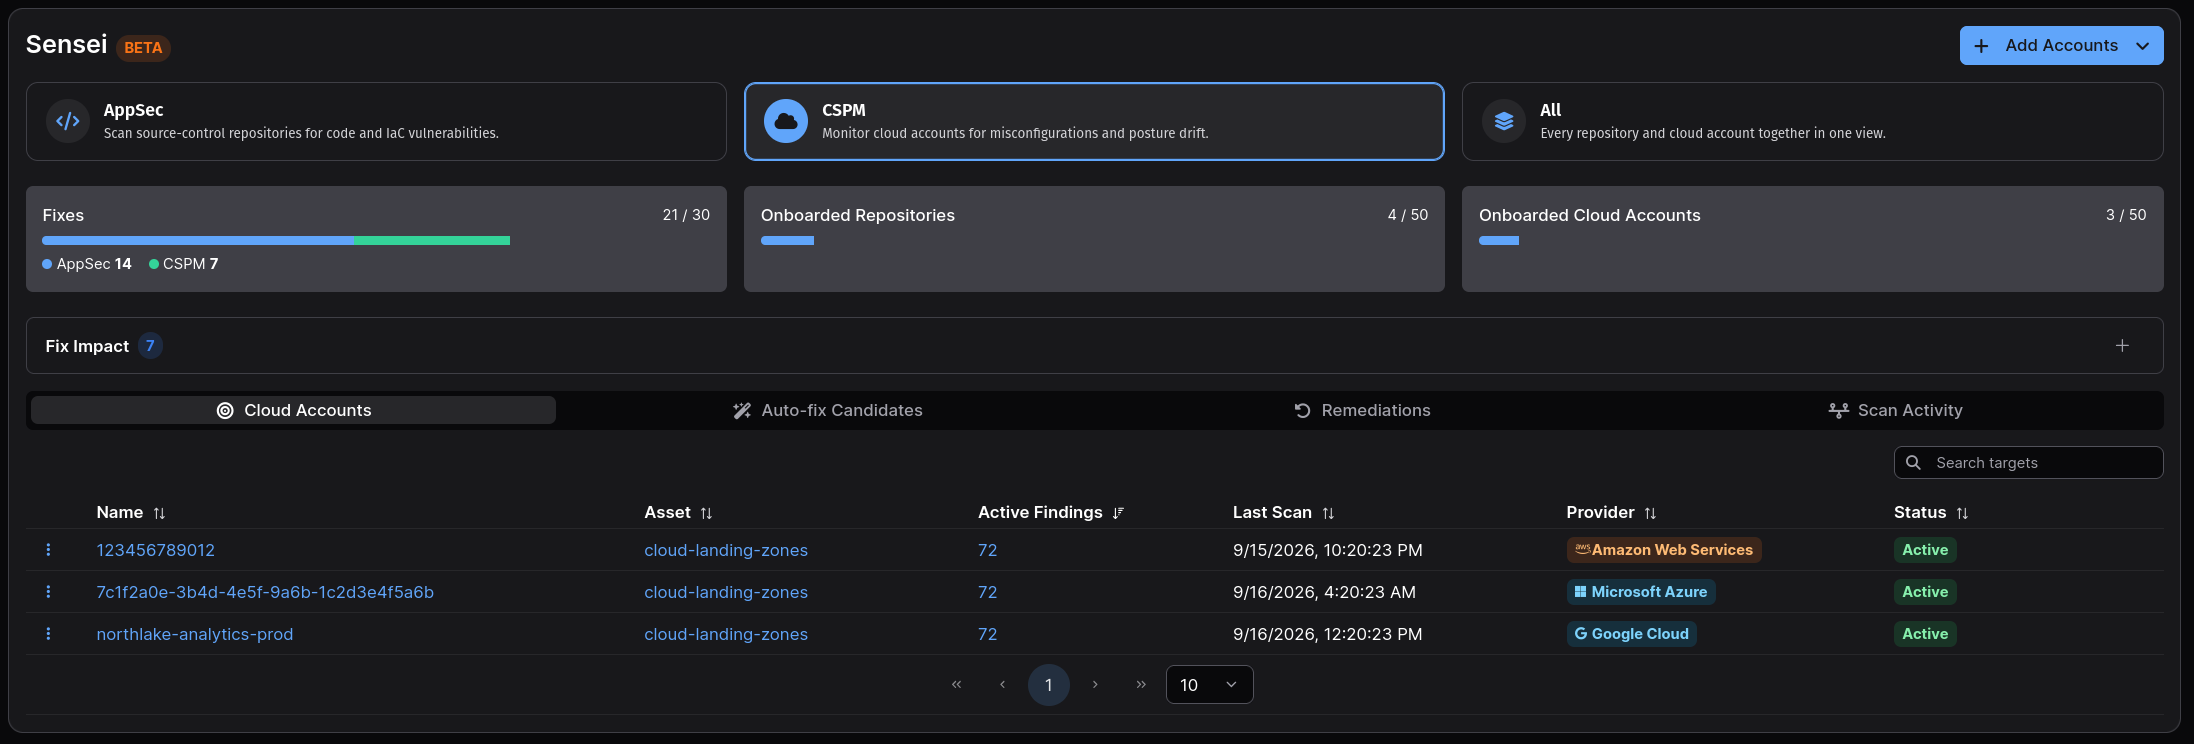
Connect AWS accounts, Azure subscriptions, and GCP projects with read-only scan credentials. A single Cloud Connection can discover every account a credential can see, across an AWS Organization, an Azure tenant, or a GCP folder, and onboard them in bulk. Every credential is encrypted at rest, and each onboarded account links to a DefectDojo Asset so its findings live alongside the rest of your security data.
Misconfiguration Scanning
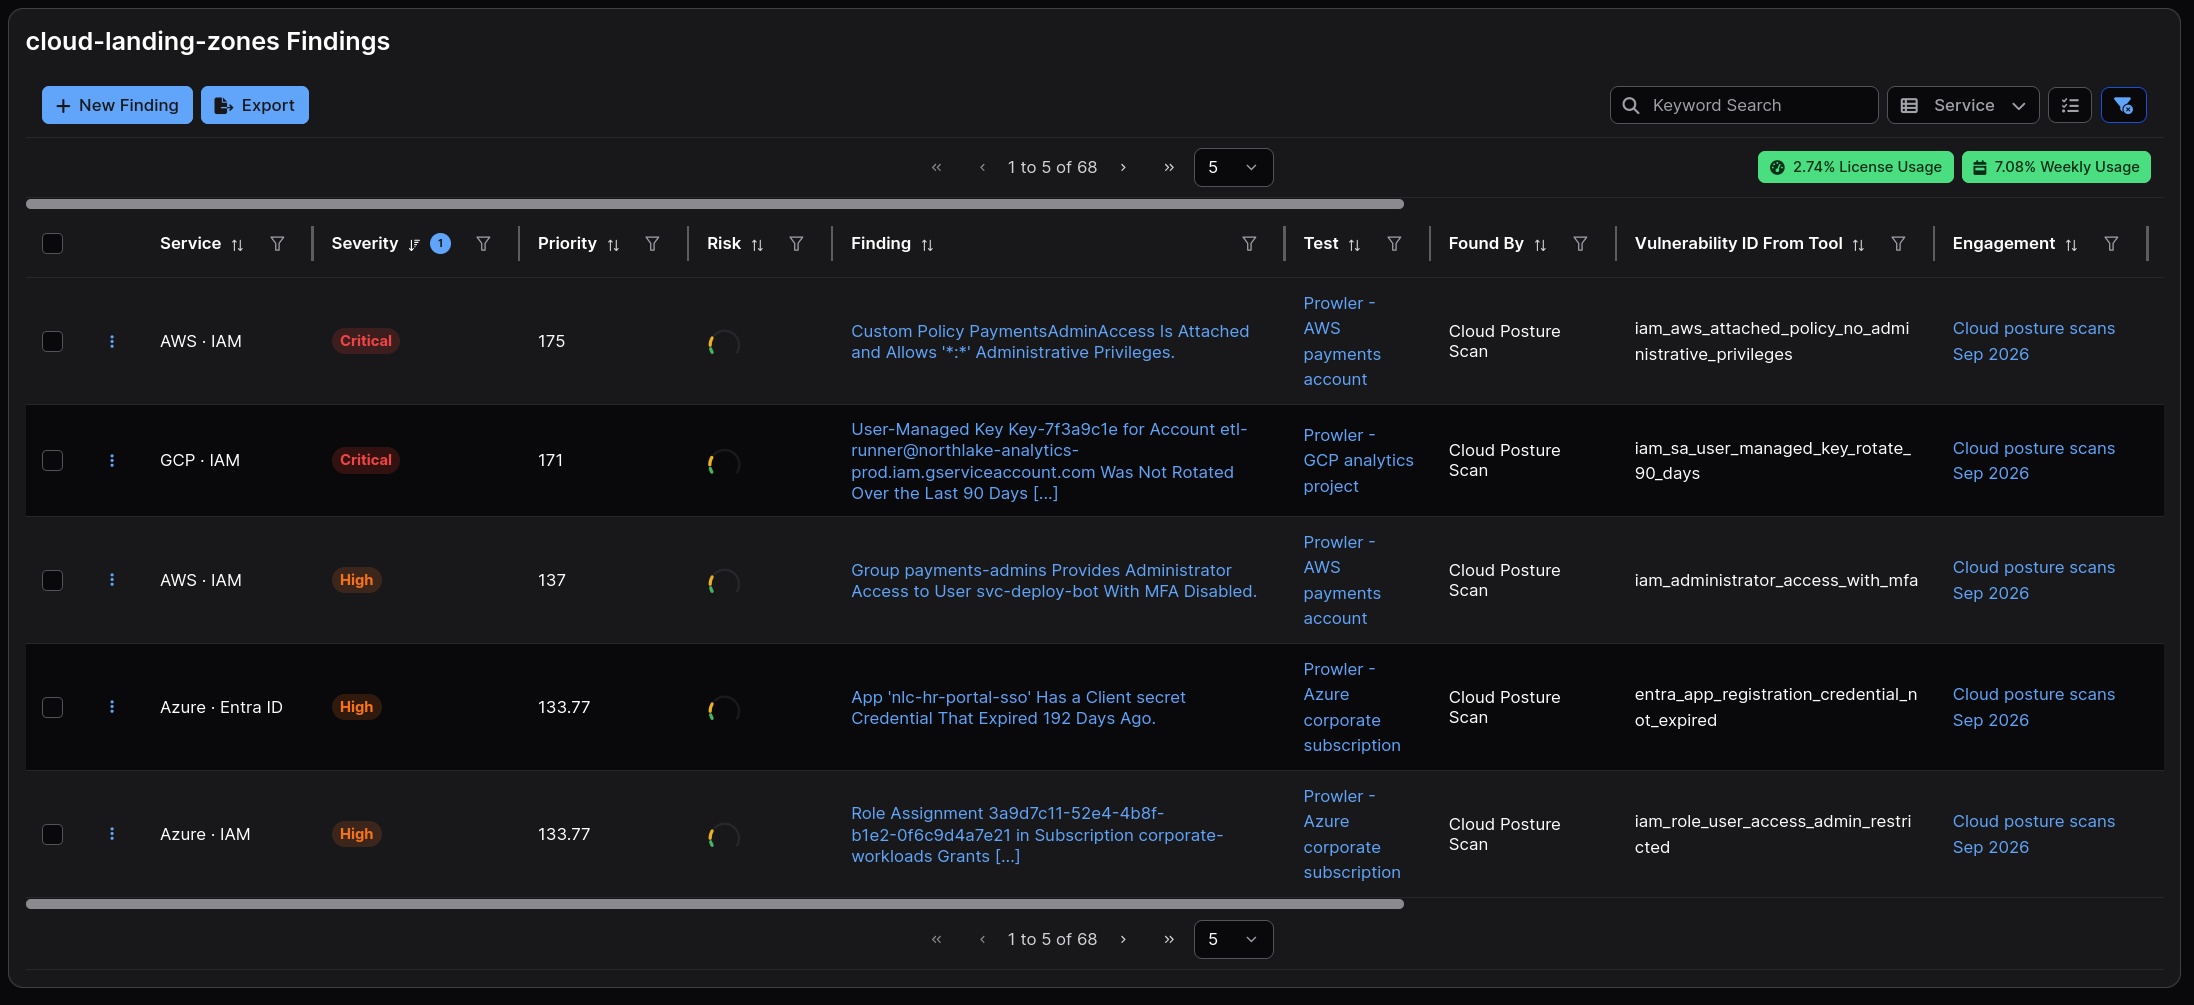
Scan any onboarded account on demand from the Sensei hub. Each misconfiguration imports as a finding recorded against the cloud resource it concerns: the S3 bucket, the security group, the storage account. Re-scans update the same findings instead of duplicating them, and large accounts are automatically scanned in shards and reconciled into one result set.
Fix in Cloud
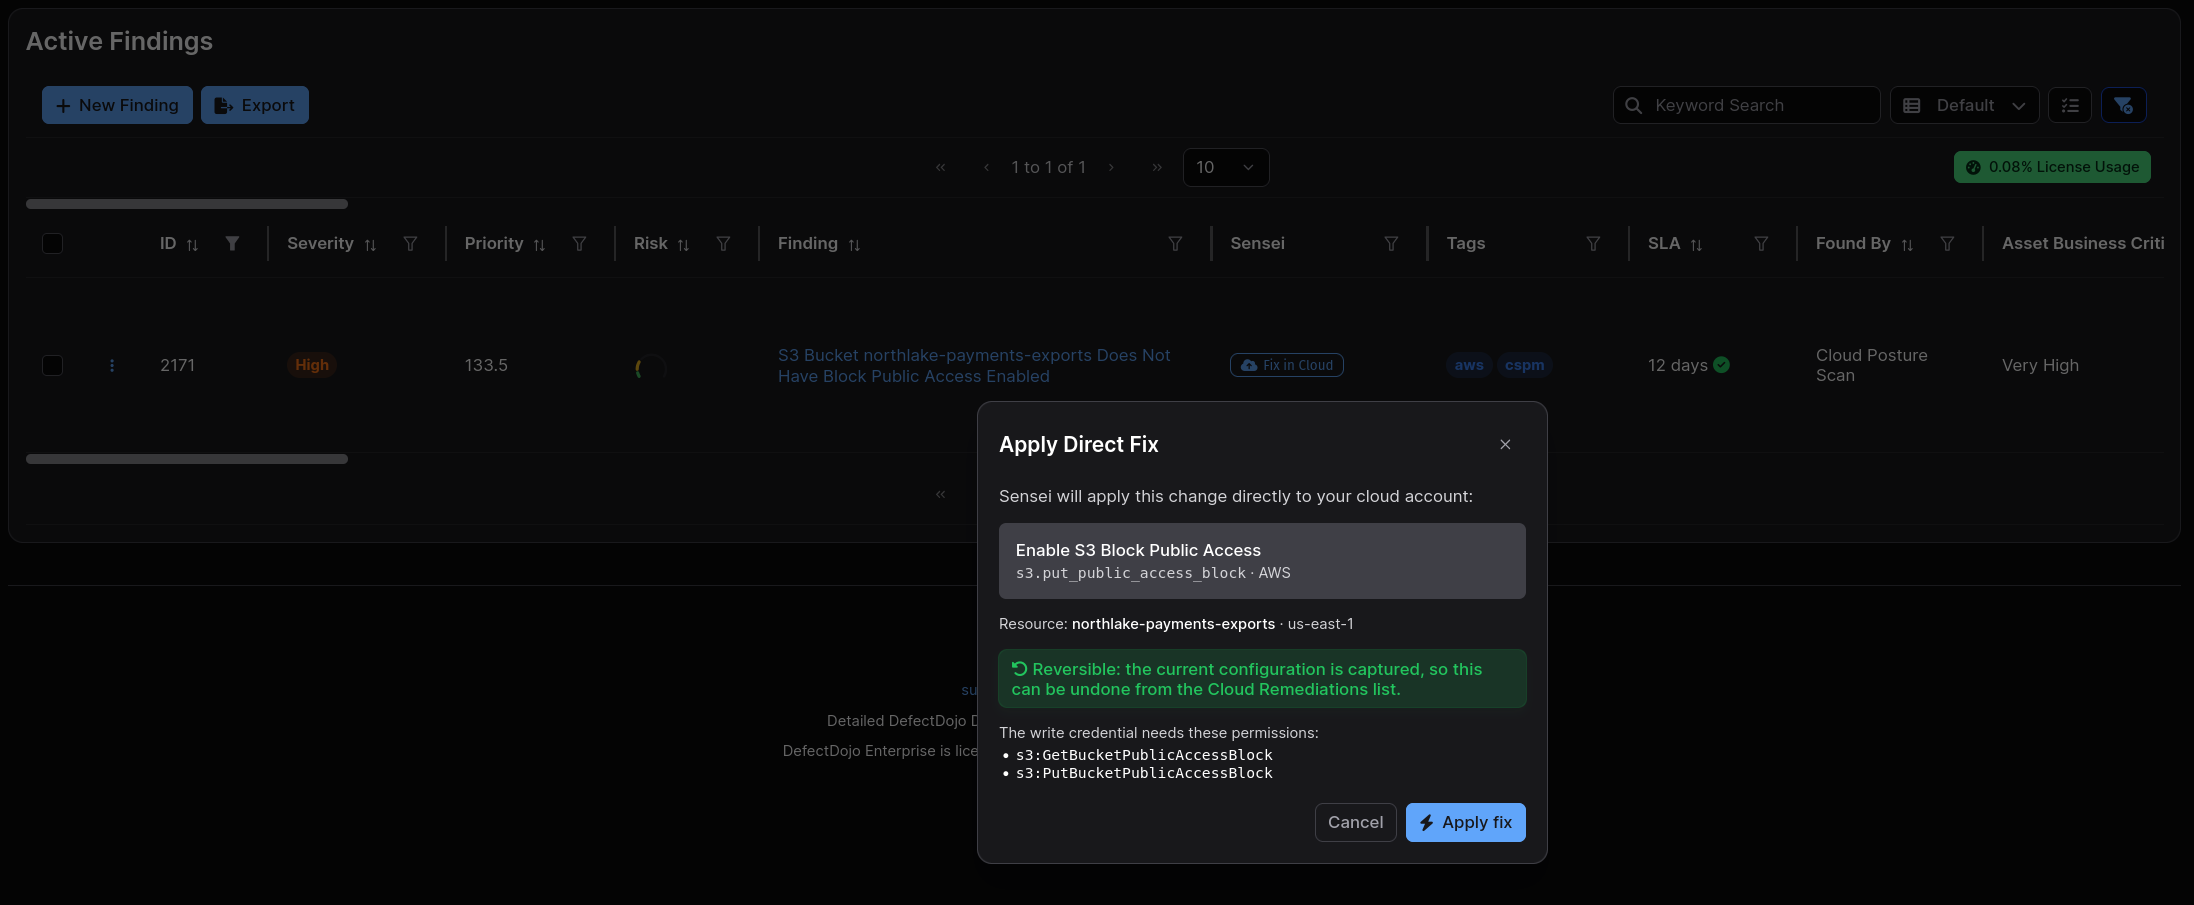
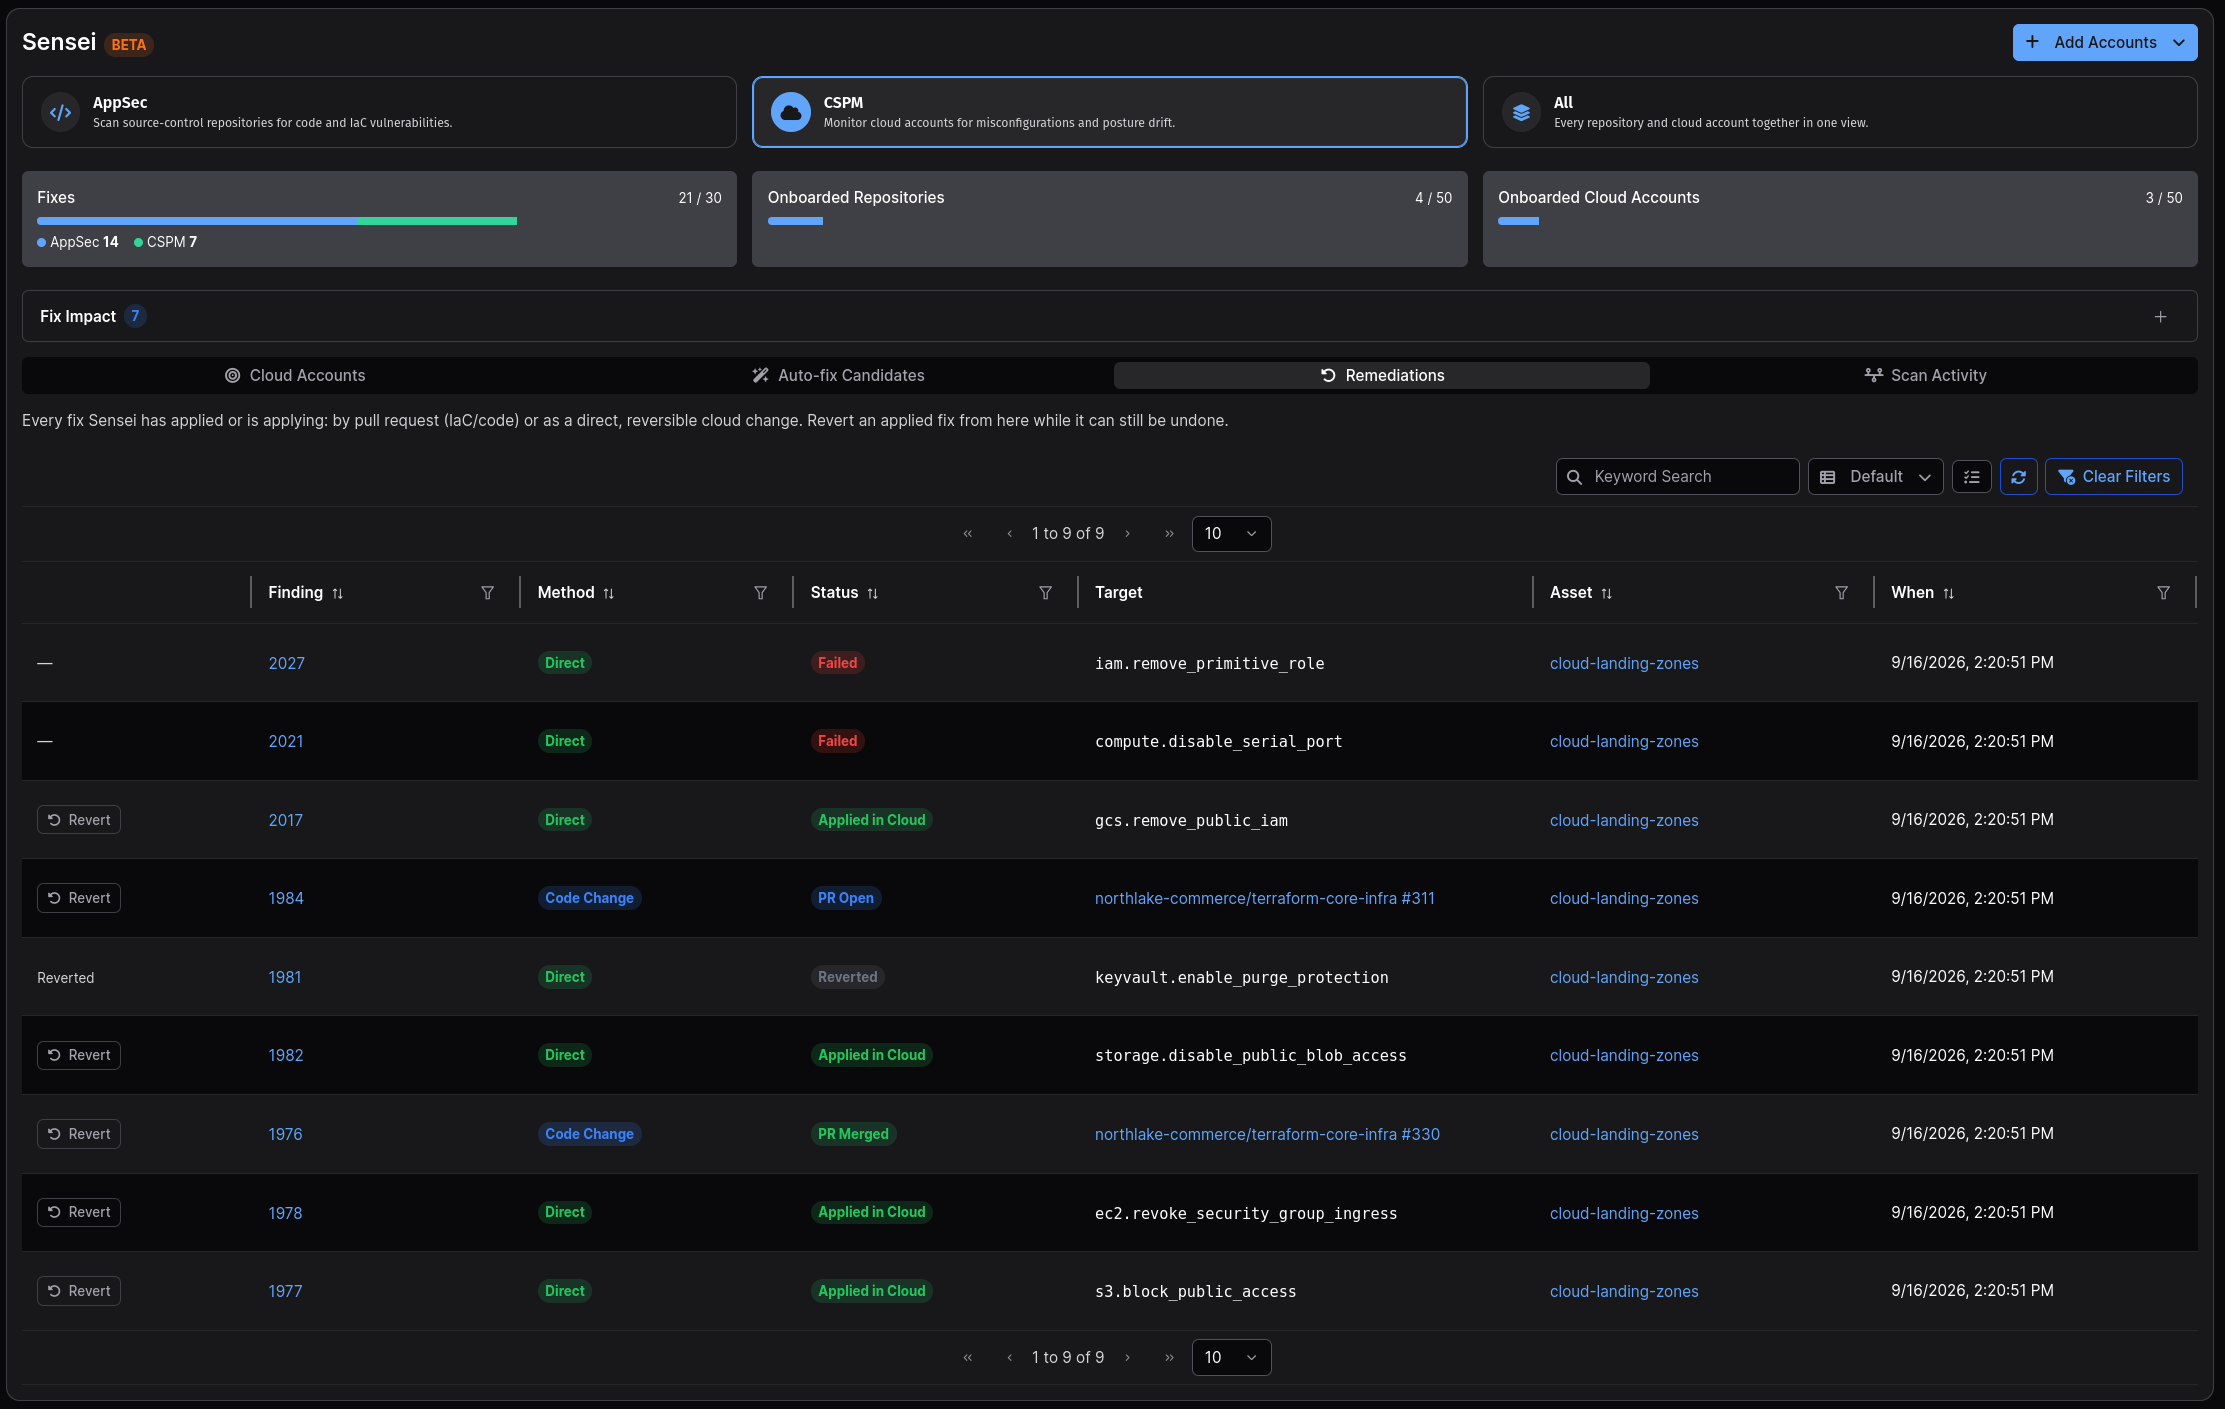
For resources that no IaC provisions, Sensei applies a direct, reversible fix through the provider API. An approval preview states the exact action, the resource it will change, and the permissions required before anything runs. Launch actions are deliberately non-destructive: block S3 public access, revoke internet-facing security group ingress, disable public blob access on an Azure storage account, and remove public IAM bindings from a GCS bucket.
IaC Pull Requests
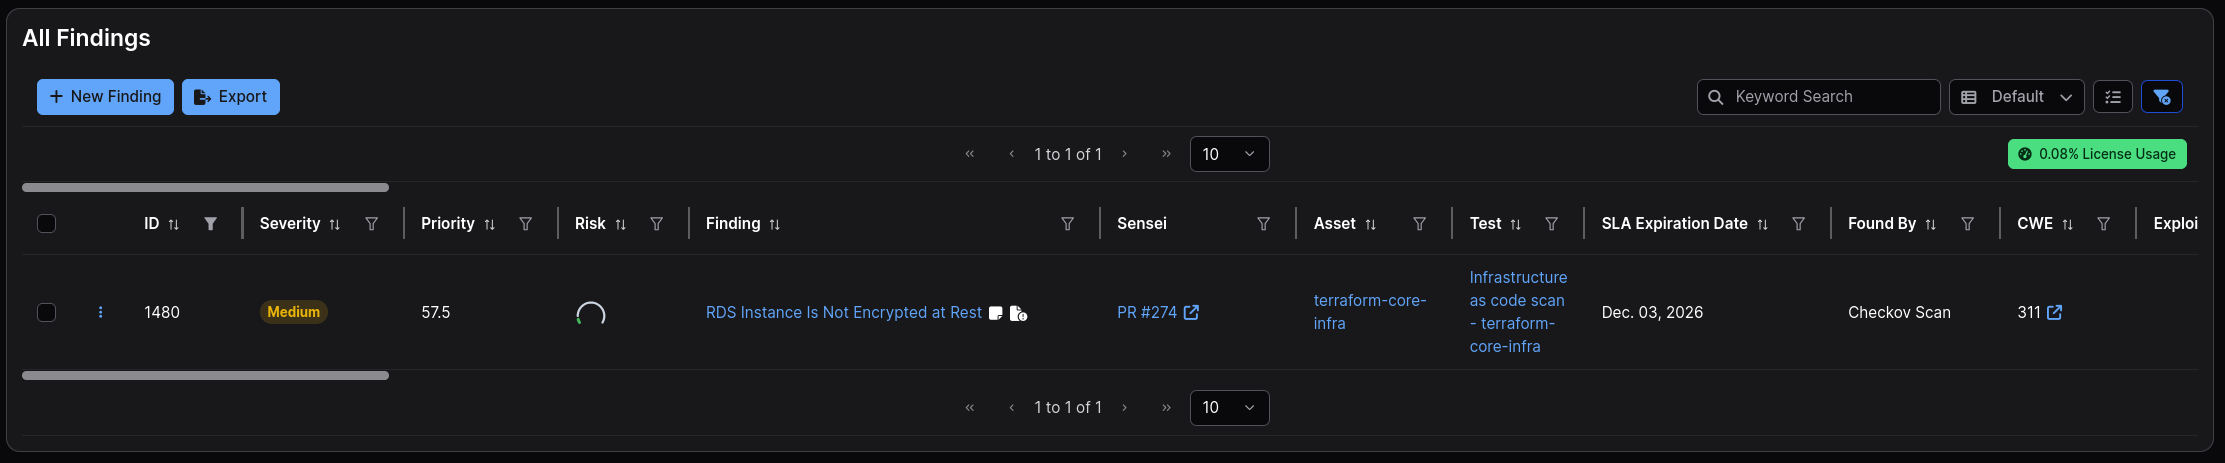
When a resource is managed as code, Sensei opens a pull request on the linked infrastructure as code repository, the same scan-and-fix flow it uses for application security findings. The finding stays open until the change lands and the next scan confirms it in the live account, so your board reflects cloud reality, not repository optimism.
Cloud Remediations Ledger
Every direct fix is recorded in an audit ledger: the action, the resource, the provider, the status, and who applied it. Sensei captures the resource's prior state before changing anything, so a reversible fix carries a working Revert button. If the live resource has drifted since the fix, the revert refuses rather than clobbering an out-of-band change.
Bring Your Existing Cloud Security Tools
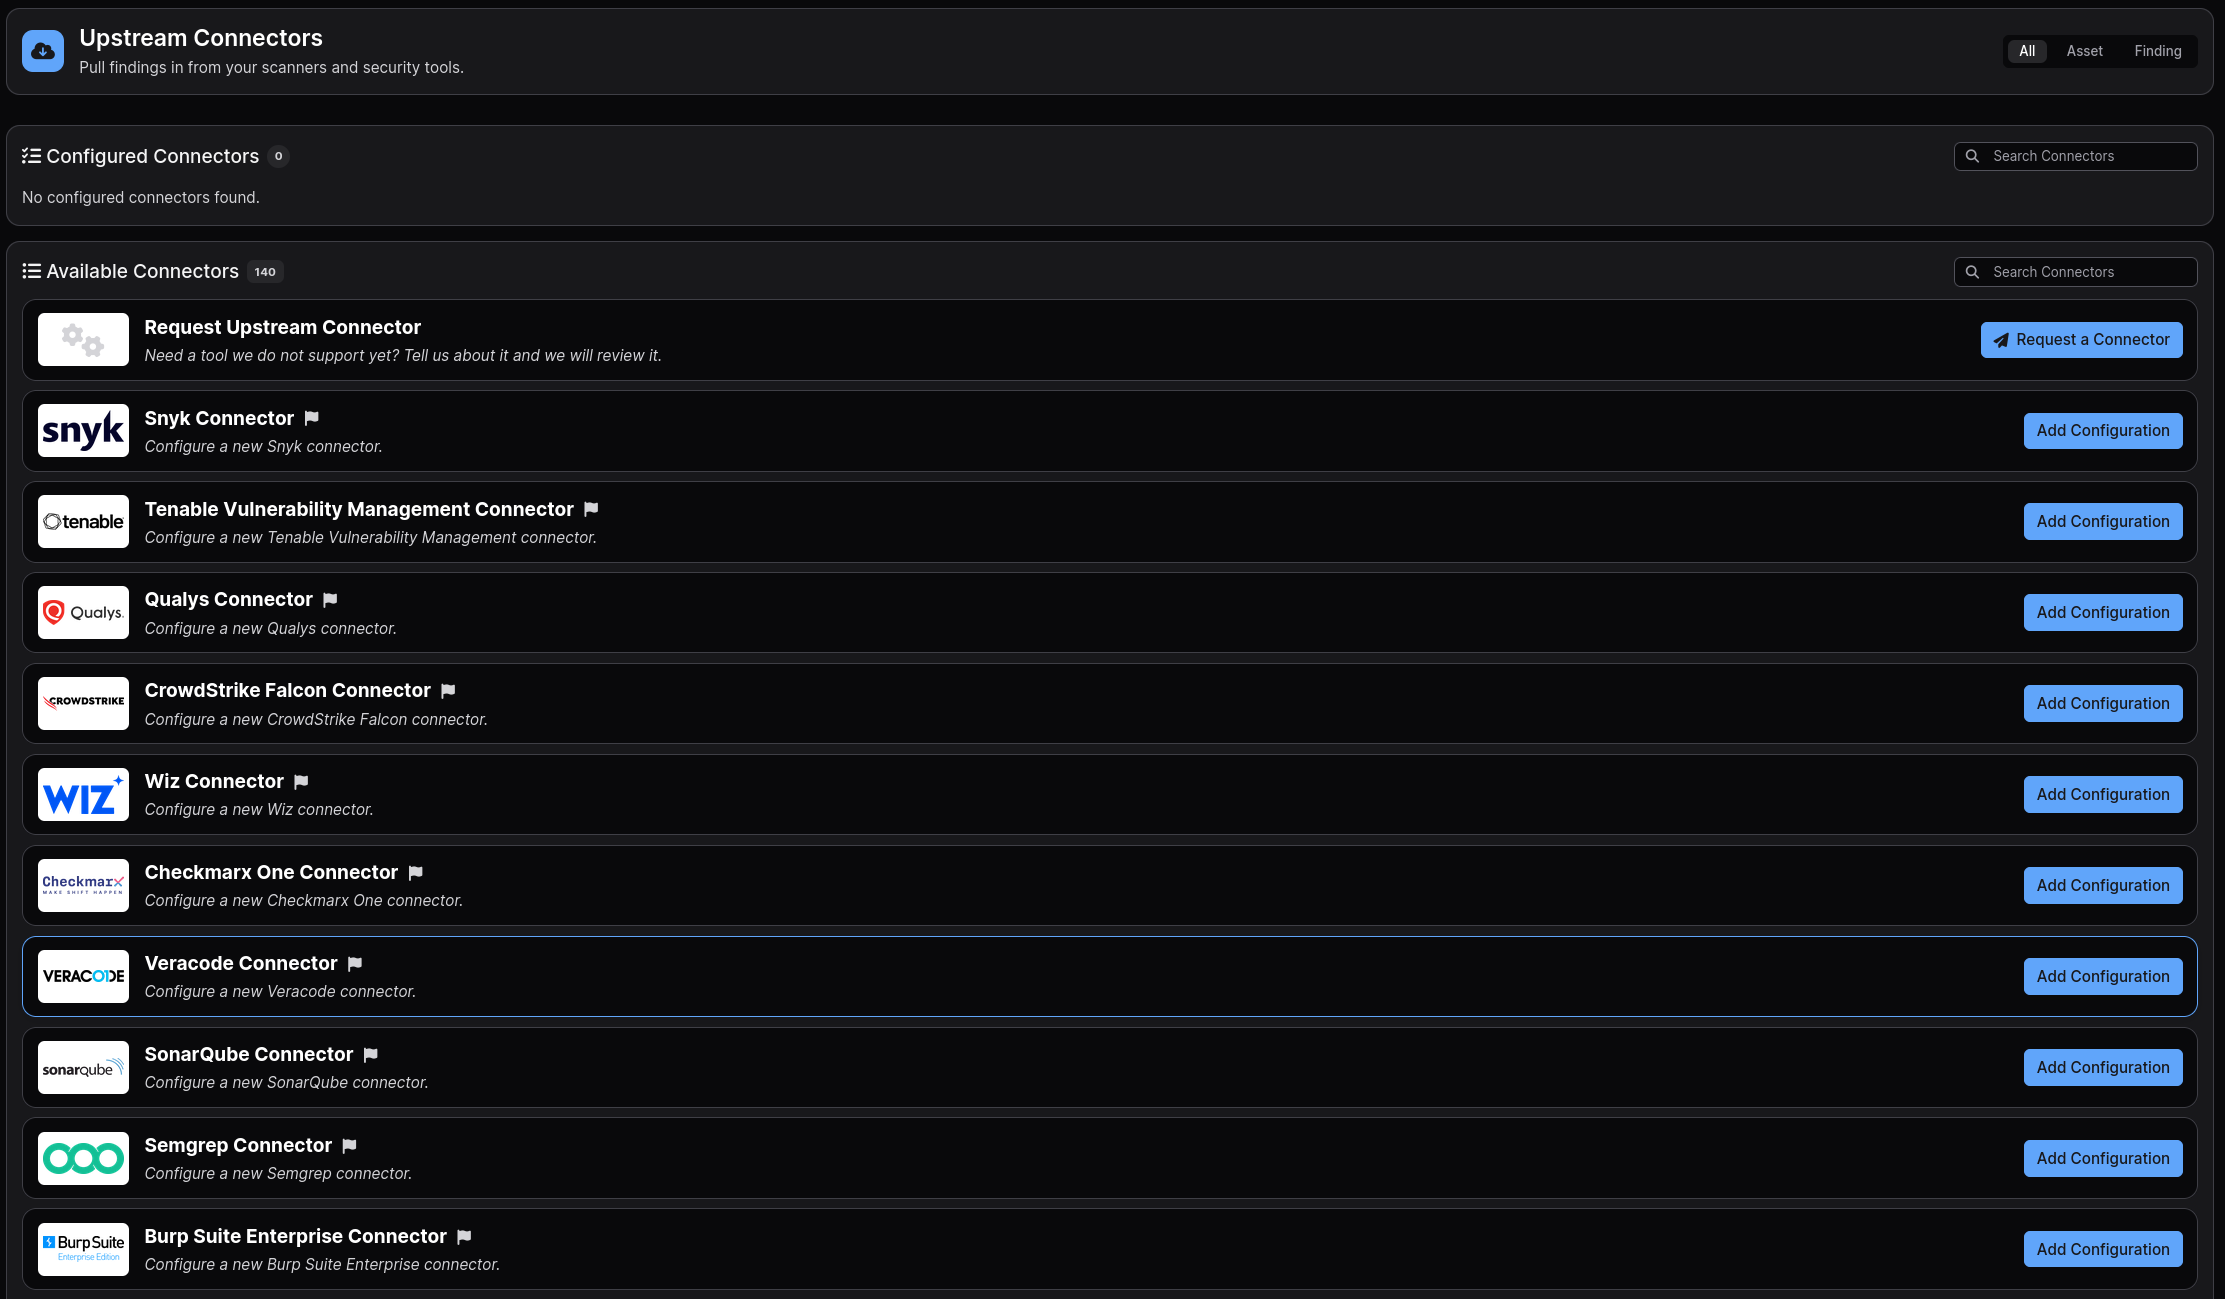
Already running Wiz, Microsoft Defender for Cloud, or another scanner? DefectDojo ingests findings from 500+ security tools, including the CSPM tools in your stack, then deduplicates and prioritizes across all of them. Your existing investment feeds the same queue, the same SLAs, and the same reporting.
One Queue for Cloud and Code.
Zero Exports.
One Platform for Cloud and Code
AppSec and CSPM share one hub. A cloud account onboards, scans, and fixes the same way a repository does, and both feed one set of findings, one prioritization engine, and one security posture report. No more explaining to leadership why cloud security and application security tell two different stories.
Fixes You Can Trust in Production
Nothing changes your cloud without a human approving it first. Scan credentials are read-only and never widened for writes; direct fixes use a separate, scoped write credential. Prior state is captured, a revert plan is recorded, and reverts are drift-checked. It is remediation built by people who have been paged at 3 a.m. by an automated tool's good intentions.
Built by Practitioners, Trusted at Scale
DefectDojo was born in the OWASP community and has been downloaded more than 50 million times. Security teams use it to aggregate findings from 500+ tools, enforce SLAs, and report on security posture and compliance across frameworks including SOC 2, PCI-DSS, and the EU Cyber Resilience Act.
From Cloud Account to Closed Finding in Five Steps
Connect a Cloud Provider
Add a read-only credential, once per account or once for many accounts through a Cloud Connection. AWS uses audit-scoped access keys, Azure a Reader service principal, GCP a viewer service account.
Discover and Onboard Accounts
Sensei enumerates the accounts the credential can reach: AWS Organizations member accounts, Azure subscriptions, GCP projects. Pick the ones to onboard, and each is linked to a DefectDojo Asset.
Scan for Misconfigurations
Run a scan on demand from the hub. Each misconfiguration lands as a finding against the specific cloud resource it concerns, and scan activity appears in the same ledger as your repository scans.
Prioritize What Matters
Cloud findings run through the same machinery as everything else in DefectDojo: deduplication, prioritization, SLA tracking, and assignment. Cloud operations and security triage one queue instead of two consoles.
Remediate and Prove It
Fix by IaC pull request or apply a reversible Fix in Cloud after an approval preview. The Cloud Remediations ledger records every direct change, its status, and who applied it, so the audit answer is a link, not an archaeology project.
Frequently asked questions
What is CSPM (cloud security posture management)?
CSPM is the practice of assessing cloud environments for misconfigurations and risky settings: public storage, internet-exposed security groups, over-permissive IAM. Misconfigurations remain one of the most common causes of cloud security incidents, and CSPM tooling exists to find them before an attacker does. DefectDojo extends CSPM past detection into prioritization and remediation.
Which cloud providers does DefectDojo CSPM support?
DefectDojo CSPM supports AWS accounts, Azure subscriptions, and GCP projects. Scanning uses read-only credentials for each provider, and a single Cloud Connection can discover and onboard many accounts at once.
Is Fix in Cloud safe to run against production?
Yes, by design. Every direct fix requires human approval through a preview that states the exact action and the permissions it needs. Launch actions are limited to non-destructive, reversible changes, prior state is captured before anything runs, and every fix is logged in the Cloud Remediations ledger with a drift-checked revert path. Destructive changes stay on the pull request path where your normal review process applies.
Can DefectDojo work with the CSPM tools we already run?
Yes. DefectDojo ingests findings from 500+ security tools, including cloud security scanners like Wiz and Microsoft Defender for Cloud, then deduplicates and prioritizes across your whole stack. You can unify your existing cloud security findings today and adopt Sensei's scan-and-fix workflow when you are ready.
Is CSPM available in Community Edition?
Sensei CSPM is a DefectDojo Pro capability. Community Edition can still import cloud scanner reports through its parsers and unify cloud security findings with the rest of your security data. If you want scanning and remediation handled inside the platform, that is DefectDojo Pro.