Compliance

Security Compliance Without the Scramble

Your auditors want evidence. Your scanners produce noise. DefectDojo closes the gap.

DefectDojo is the open-source unified vulnerability management platform that turns raw AppSec findings into documented, audit-ready proof of your security program. Aggregate every scanner, enforce remediation SLAs, and generate compliance reports on demand instead of rebuilding spreadsheets every audit cycle.

The problemEvidence that builds itself

Compliance Is a Data Problem. Treat It Like One.

Every security compliance framework asks the same core questions: what vulnerabilities exist, how fast do you fix them, and can you prove it?

Most AppSec teams can't answer those questions without a fire drill. Findings live in a dozen disconnected scanners. Remediation timelines live in tickets. Exceptions live in email threads. When the audit arrives, someone spends weeks stitching it all together by hand.

DefectDojo ends that cycle. It aggregates findings from your entire security stack into a single system of action, then deduplicates, enriches, and tracks every finding through its full lifecycle. Every import, status change, risk acceptance, and remediation is recorded. Your compliance evidence builds itself as your team does the work, so audit readiness becomes a byproduct of good security instead of a separate project.

Security teams use DefectDojo to report on security posture and compliance across frameworks including SOC 2, PCI-DSS, and the EU Cyber Resilience Act.

Everything You Need to Prove Your Security Posture

Unified System of Action

Parse findings from 500+ security tools into one platform. When every SAST, DAST, SCA, container, and infrastructure finding lands in one place, your compliance reporting covers your actual attack surface, not just the tools someone remembered to export.
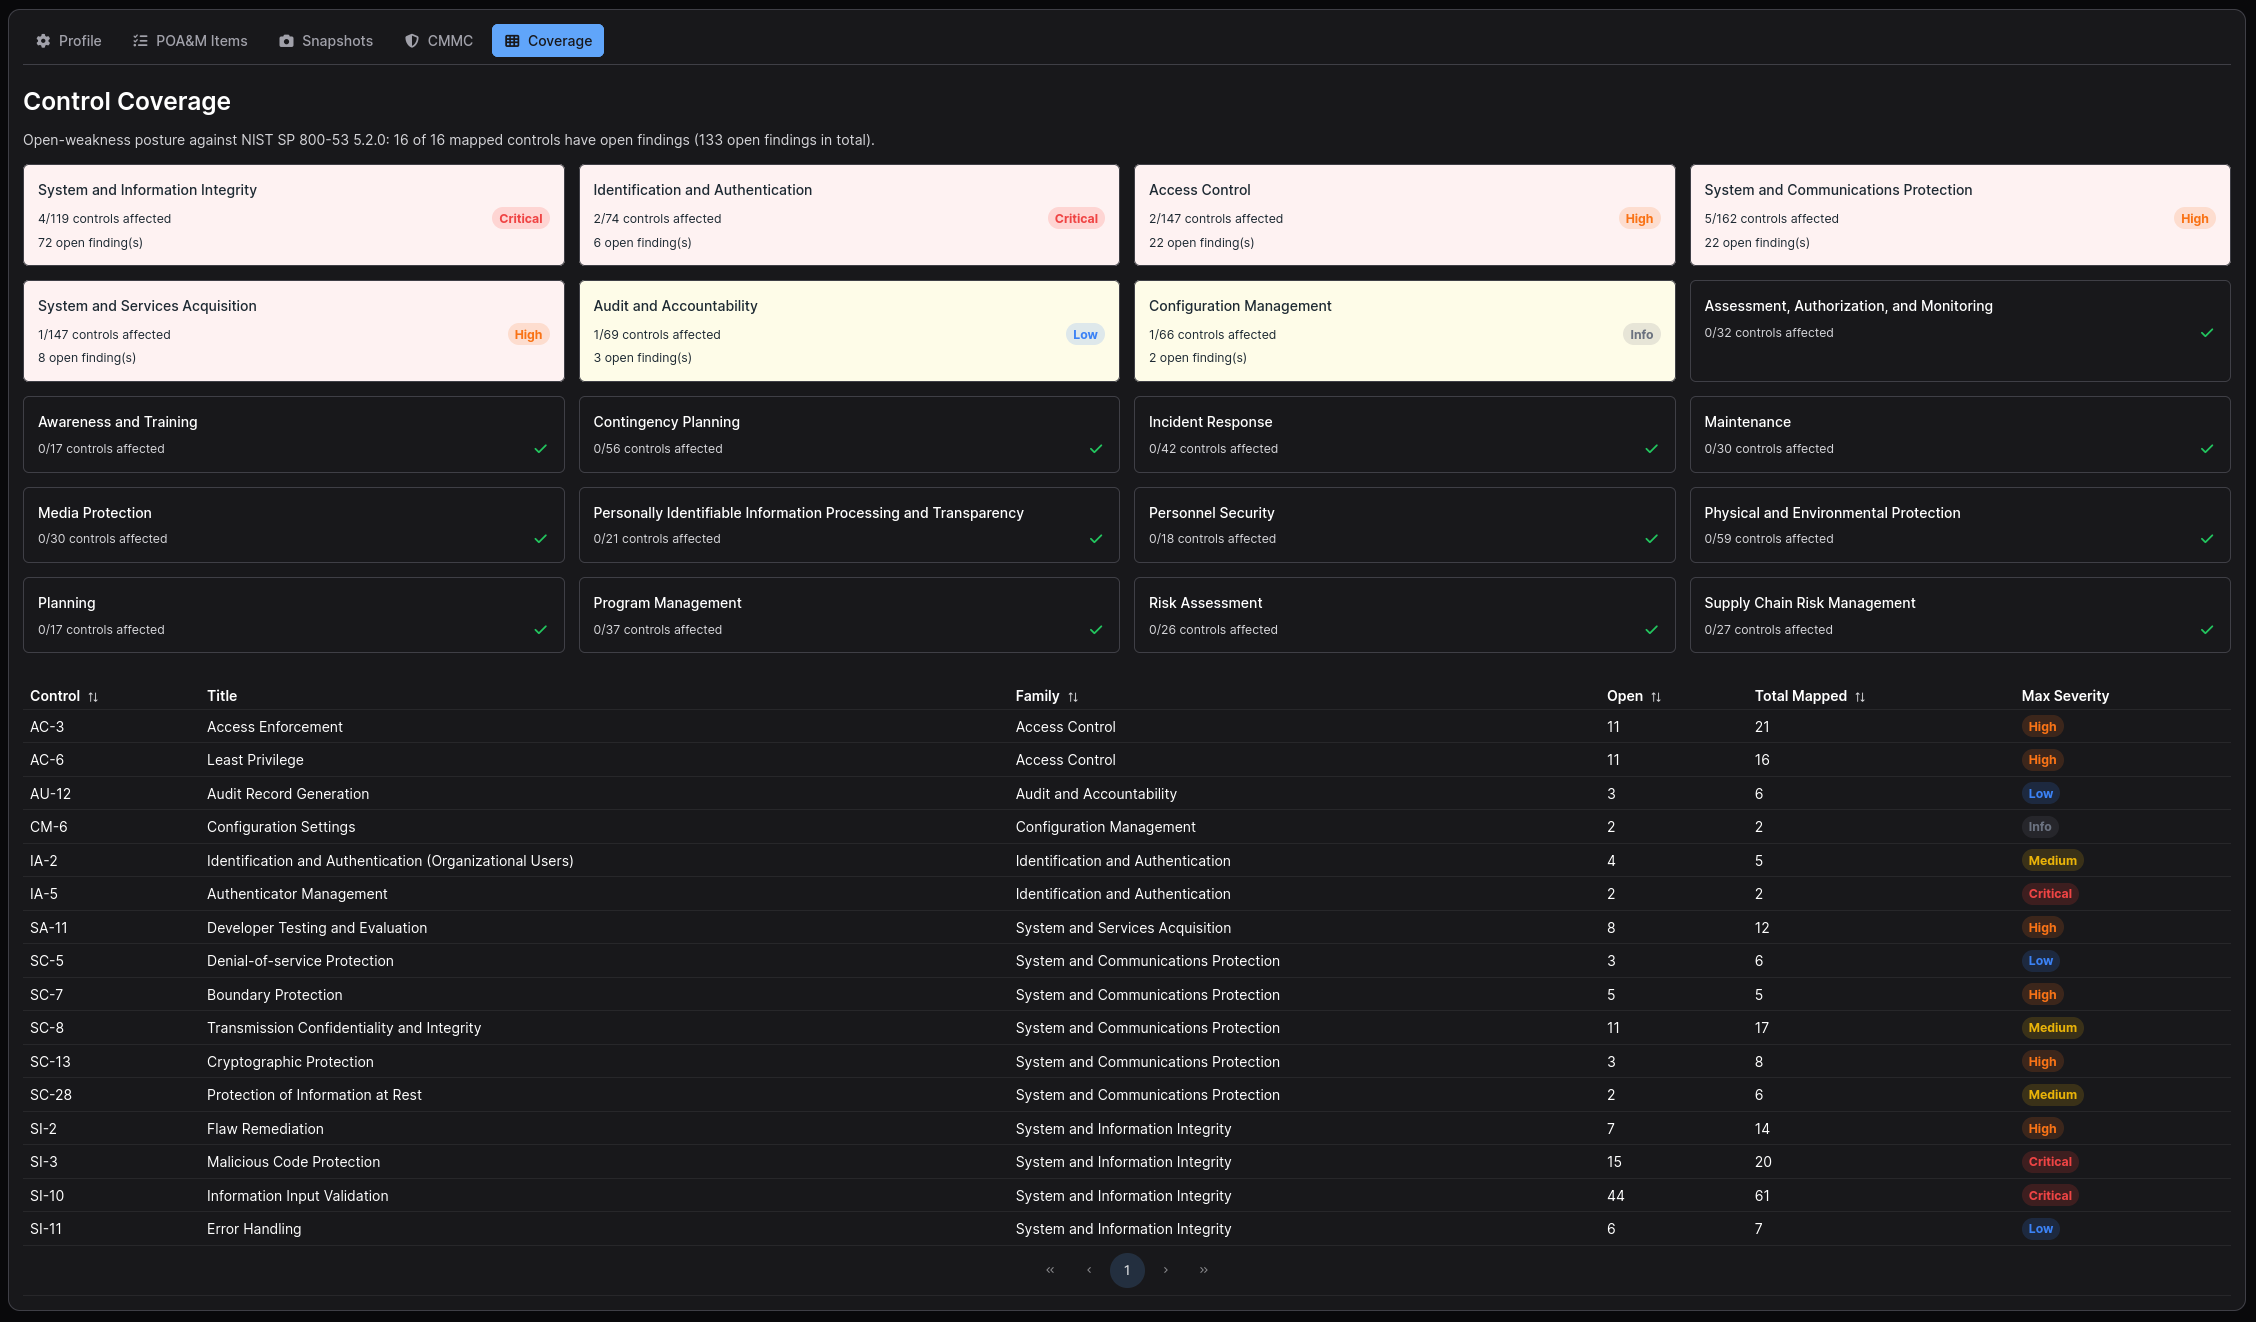
Unified System of Action

SLA Enforcement and Tracking

Define remediation SLAs per Product, based on severity or risk. DefectDojo counts down every finding against its deadline, flags breaches automatically, and tracks whether findings were mitigated within SLA. Your remediation policy stops being a document and starts being enforced.
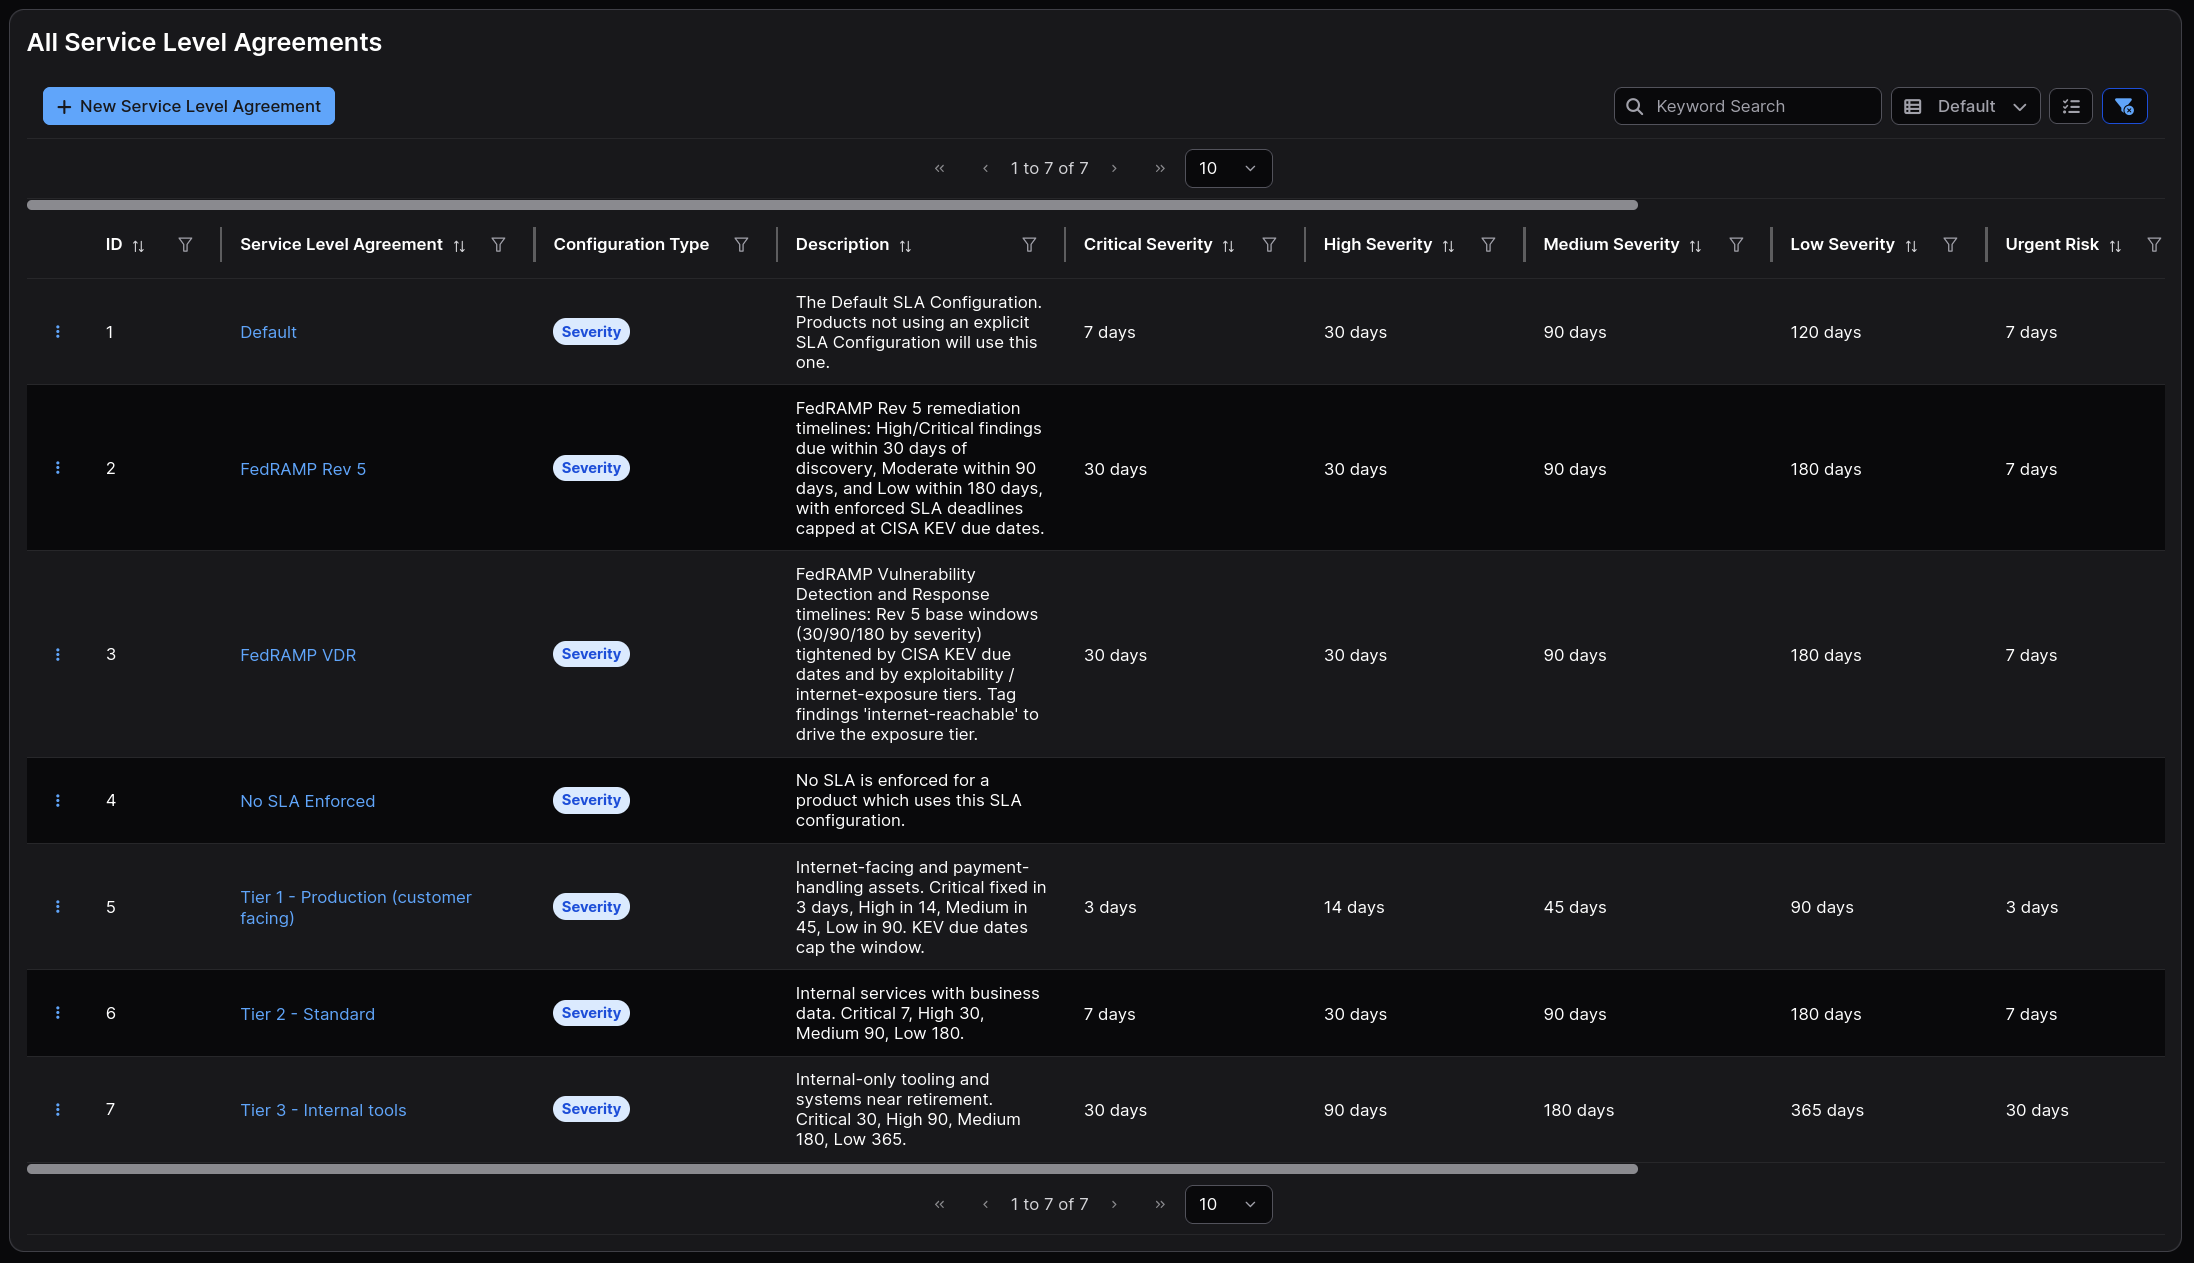
SLA Enforcement and Tracking

Custom Compliance Reports

Build branded, audience-ready reports with the Report Builder. Scope reports to a Product Type, Product, Engagement, or Test, include executive summaries with SLA performance, and save templates so the next audit takes minutes, not weeks.
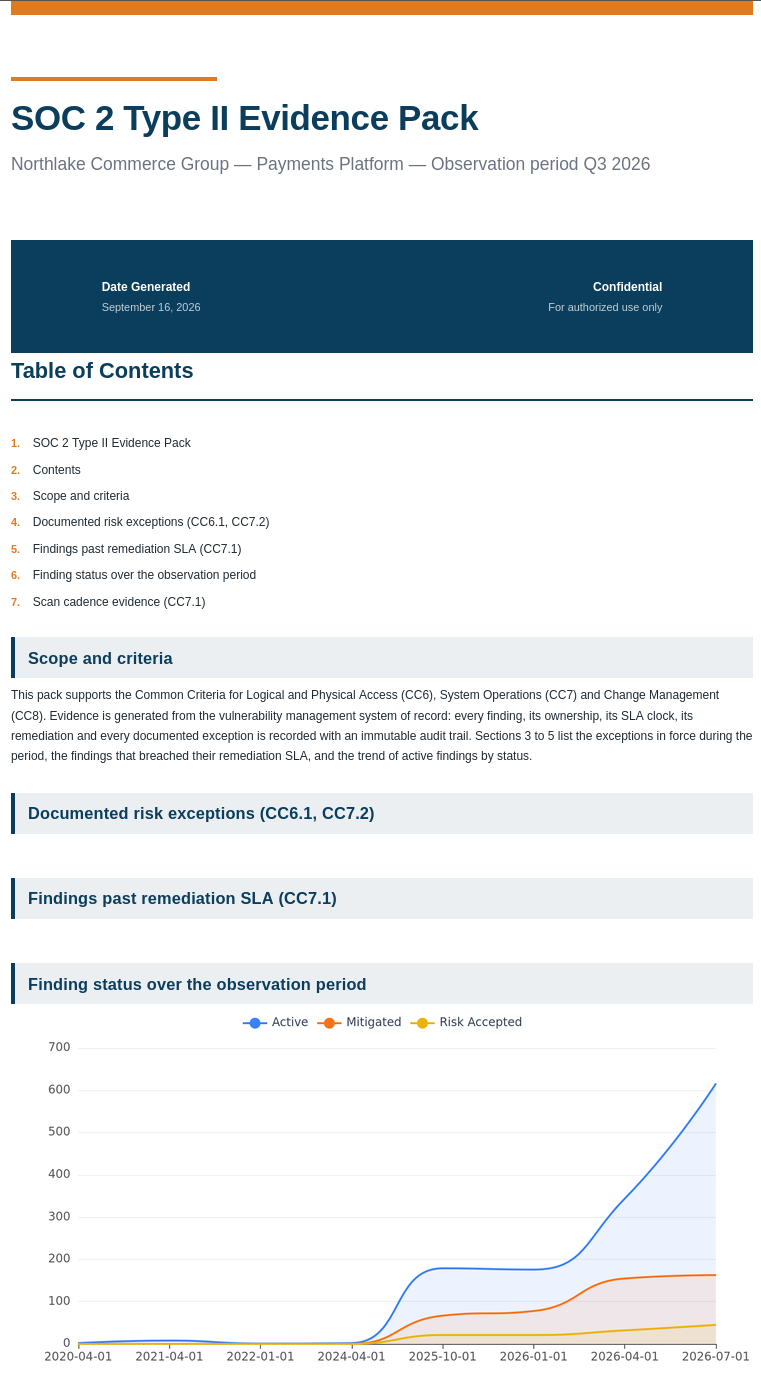
Custom Compliance Reports

Audit Logging and Object History

Every Product, Engagement, Test, Finding, and Risk Acceptance carries its own recorded history. DefectDojo Pro adds a dedicated audit log API for instance-wide activity, giving auditors the traceability they ask for without manual reconstruction.
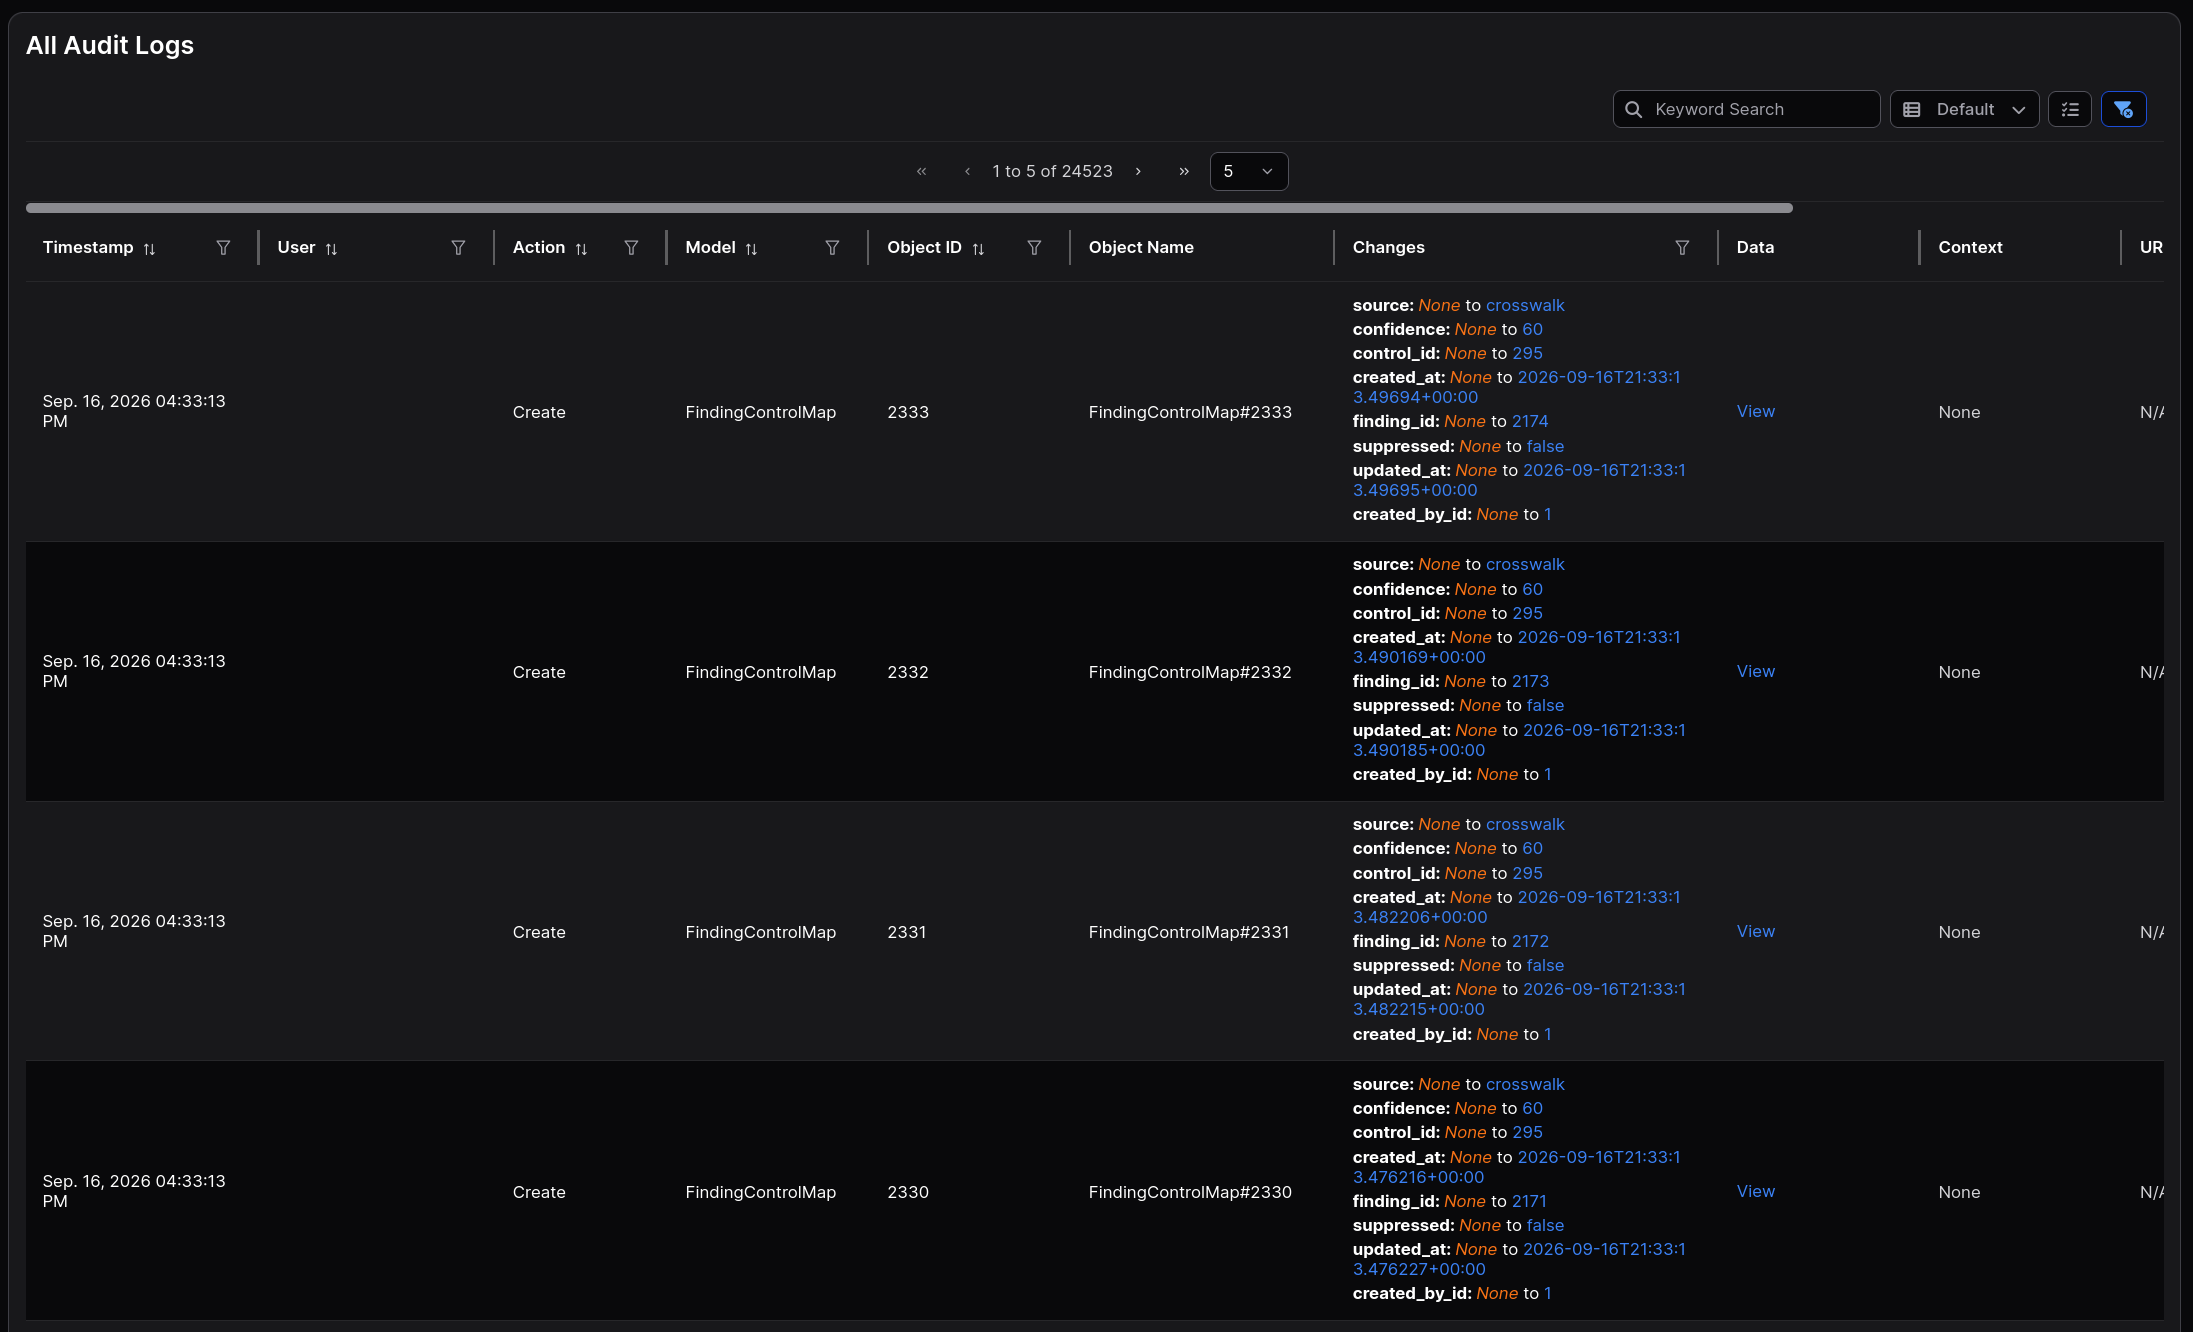
Audit Logging and Object History

Documented Risk Acceptance

Not every finding gets fixed immediately, and auditors know it. DefectDojo formalizes risk acceptance with expiration dates and automatic follow-up, so exceptions are governed decisions with a paper trail instead of forgotten liabilities.
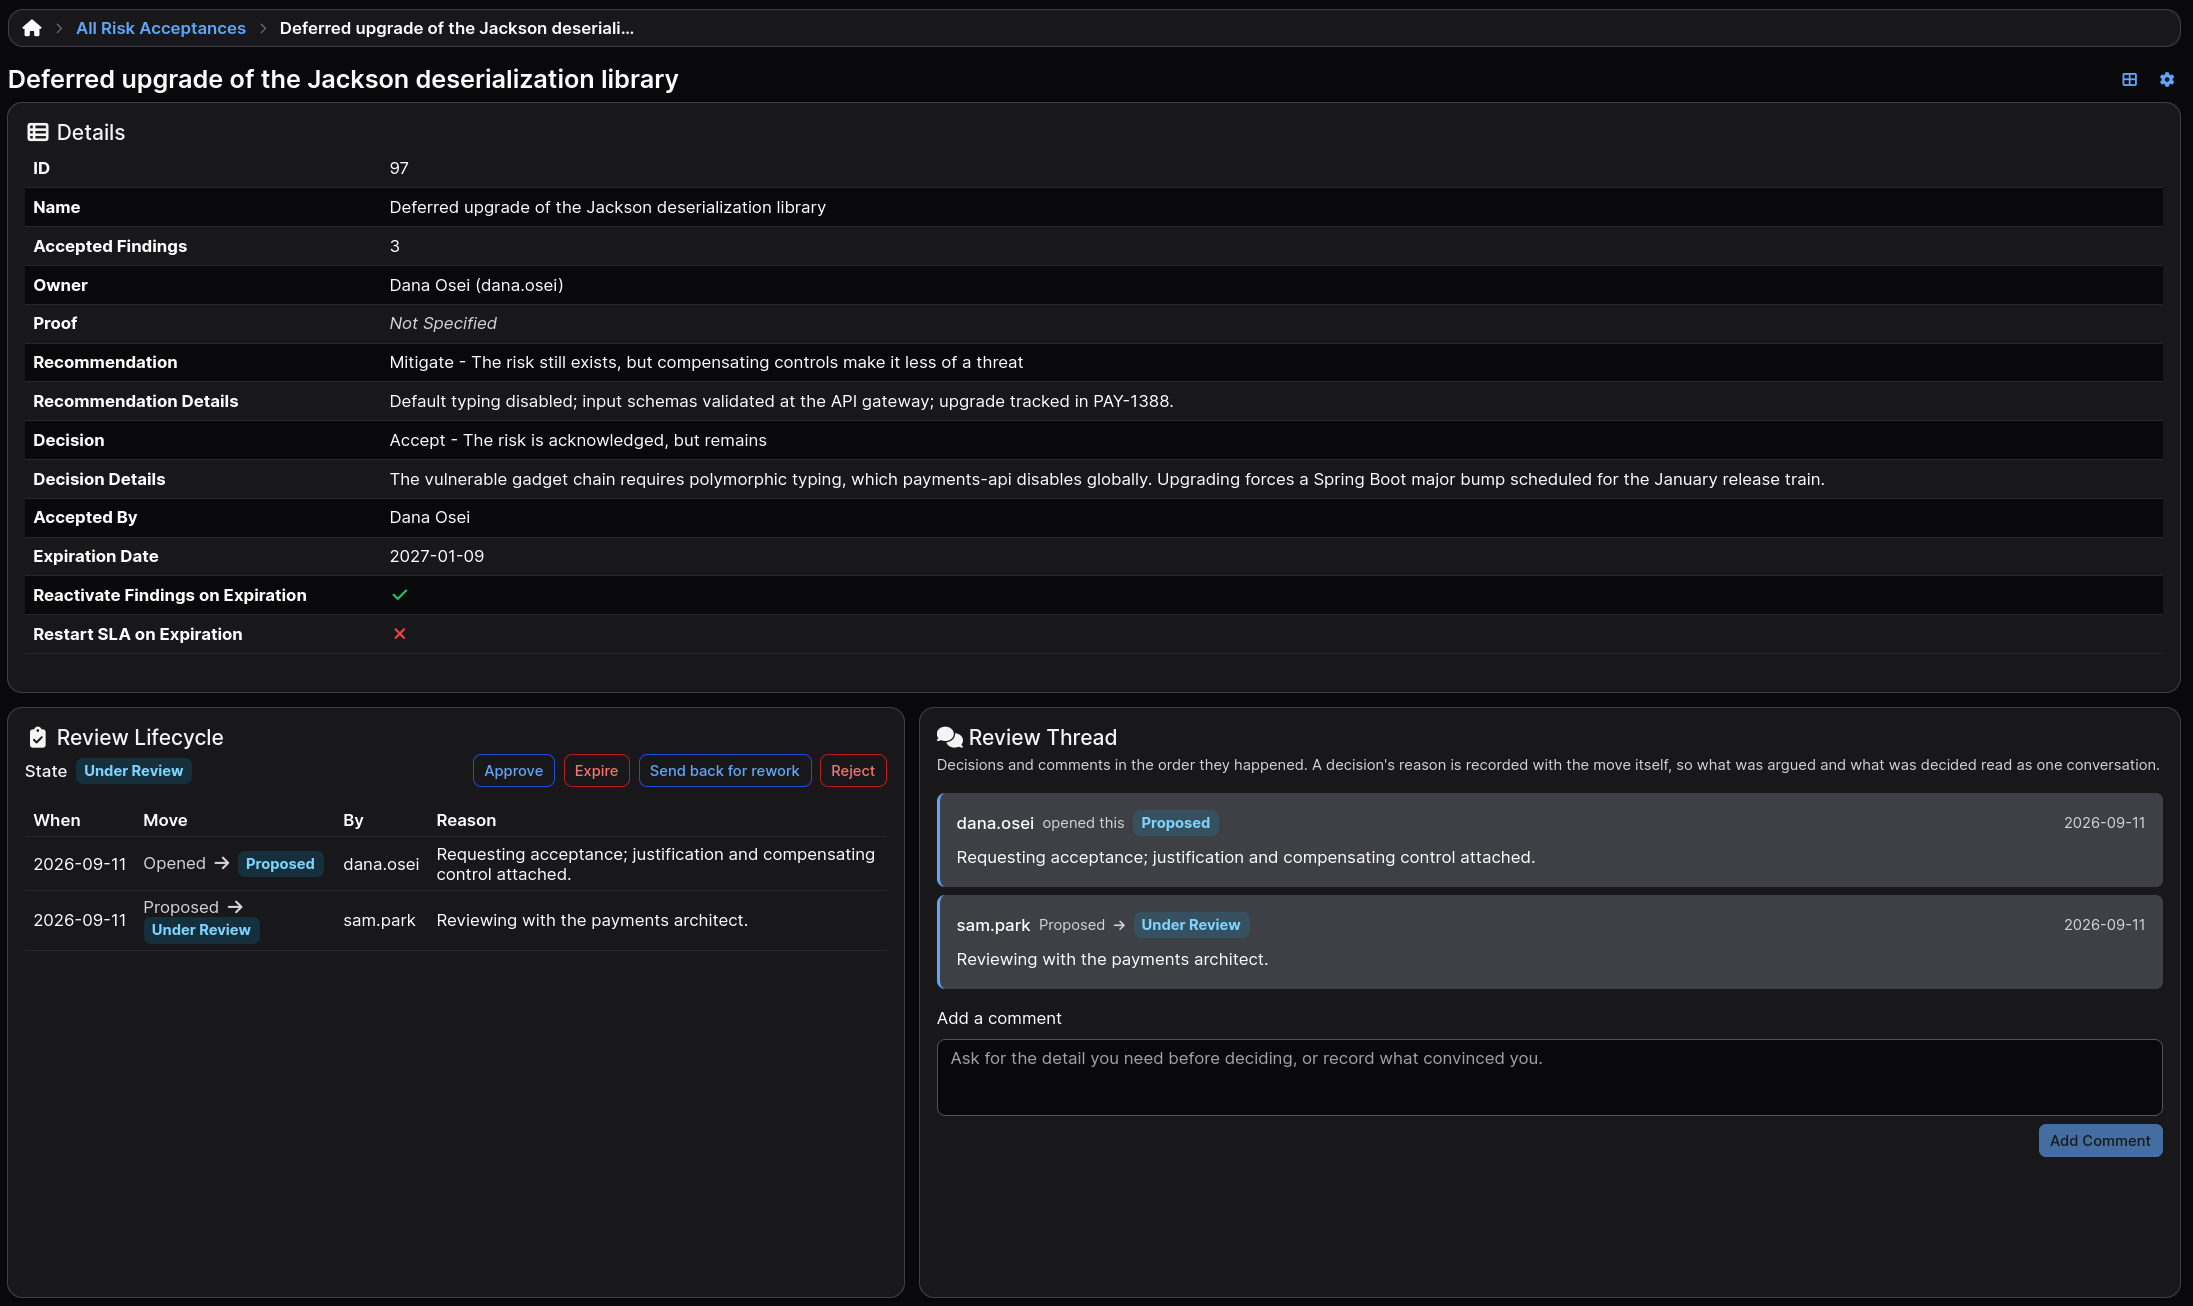
Documented Risk Acceptance

Metrics That Stand Up to Scrutiny

Executive Insights and Remediation dashboards in DefectDojo Pro show SLA performance, remediation velocity, and security posture trends at a glance. Walk into any review, board meeting, or audit with numbers you can defend.
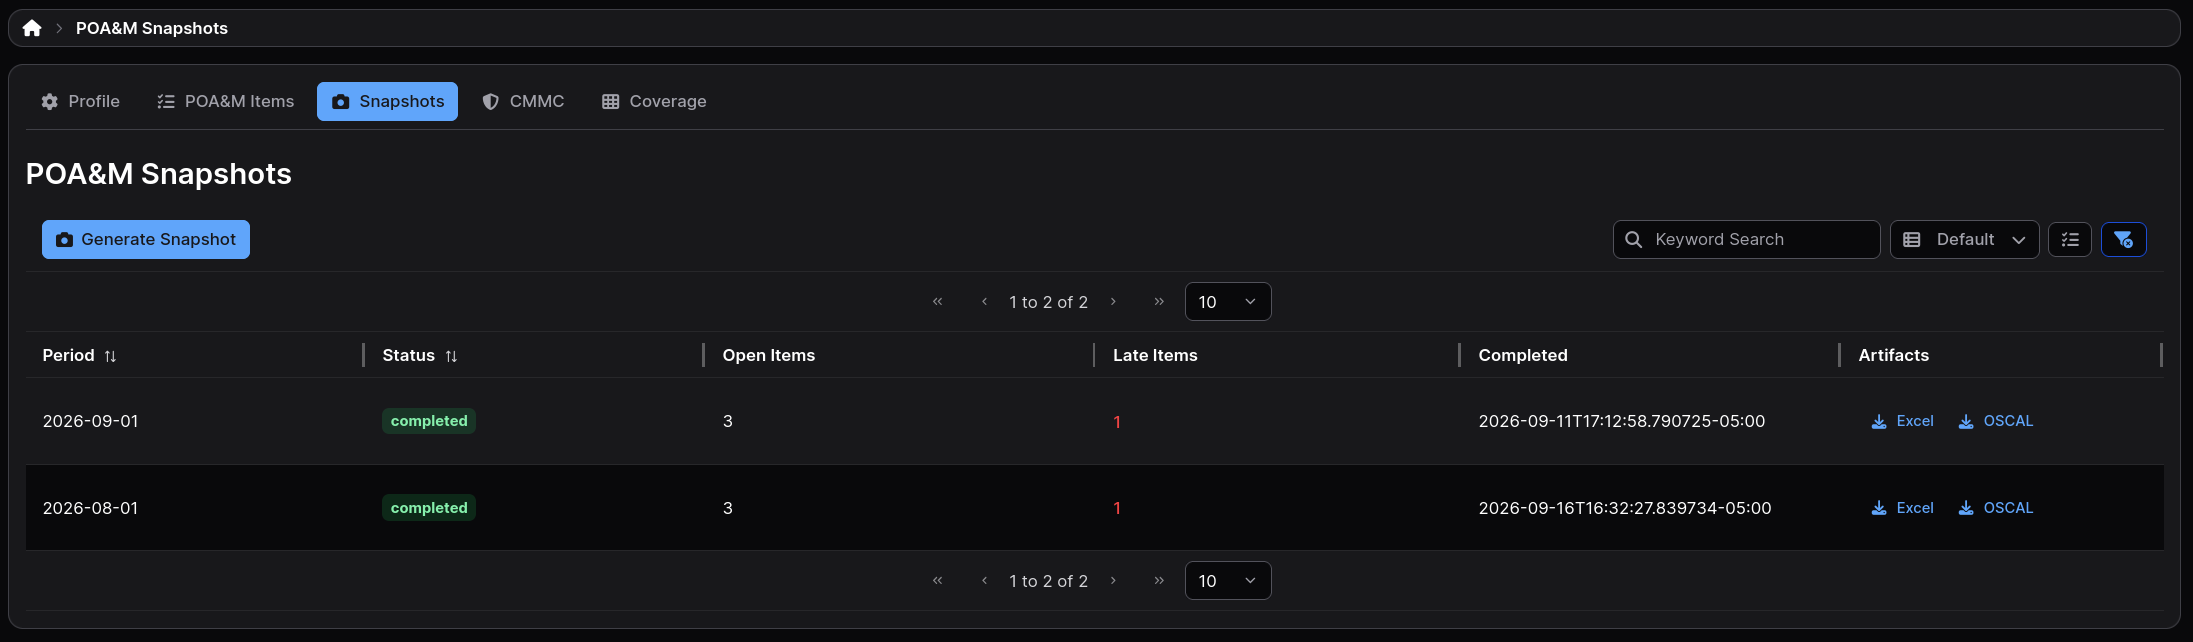
Metrics That Stand Up to Scrutiny
Why DefectDojo Audit-ready by default

Why DefectDojo for Compliance

Built by practitioners who sat through the audits.

Born from the OWASP Community

DefectDojo wasn't designed by a compliance vendor guessing at AppSec workflows. It was built by security practitioners who lived the audit scramble and automated their way out of it. That heritage shows in every workflow.

Open Source You Can Verify

Available under an OSI license, DefectDojo's Community Edition gives your team full visibility into the platform holding your security data. For regulated environments, DefectDojo Pro deploys in the cloud, on-premises, or fully air-gapped.

One Platform, Every Framework

Whether you're pursuing SOC 2, maintaining PCI-DSS, or preparing for the EU Cyber Resilience Act, the underlying evidence is the same: findings, timelines, and remediation proof. DefectDojo maintains that evidence continuously, so a new framework means a new report, not a new program.

Compliance That Scales

From a single practitioner running Community Edition to enterprises tracking millions of findings across hundreds of teams, DefectDojo's asset hierarchy keeps compliance reporting organized at any scale.

Automation Over Heroics

Deduplication, SLA countdowns, breach notifications, and Jira sync run automatically. Your team spends its time remediating real risk while the compliance evidence accumulates in the background.

How it works Five steps

From Scanner Output to Audit Evidence in Five Steps

01

Aggregate Every Finding

Import results from 500+ security tools via parsers, API, or CI/CD integration. DefectDojo normalizes everything into a consistent finding format, then deduplicates so your reports reflect unique risk instead of repeated noise.

02

Organize Around Your Business

Map findings to your real structure using DefectDojo's asset hierarchy: Organization, Asset, Engagement, Test, and Finding. Auditors think in terms of systems and business units. Your reporting will too.

03

Enforce Your Remediation Policy

Assign SLA configurations to each Product, tuned by severity or risk. DefectDojo tracks every finding against its deadline, notifies owners before and after breaches, and records whether each finding was mitigated within SLA.

04

Govern the Exceptions

Route accepted risks through formal Risk Acceptance workflows with expiration dates. When an acceptance expires, DefectDojo follows up automatically, including comments pushed to linked Jira issues until the item is resolved.

05

Report On Demand

Generate custom reports scoped to any level of your hierarchy. Include executive summaries, SLA performance, severity definitions, and your own branding. Save the template, and the next request from your auditor, customer, or board is a few clicks away.

Frequently asked questions

Which compliance frameworks does DefectDojo support?

DefectDojo supports security compliance reporting across frameworks including SOC 2, PCI-DSS, and the EU Cyber Resilience Act. Because DefectDojo maintains a continuous record of findings, remediation timelines, and risk decisions, that same evidence base supports internal policies and customer security questionnaires as well.

Does DefectDojo replace my GRC platform?

No, and it isn't trying to. GRC platforms manage policies and controls. DefectDojo owns the technical vulnerability evidence those controls depend on: what was found, when, how severe it was, and how fast it was fixed. Many teams feed DefectDojo data into their GRC workflows via the REST API.

How does DefectDojo help with audit preparation?

Every object in DefectDojo, from Products to individual Findings, carries a recorded history of changes. Combined with SLA tracking, risk acceptance records, and the Report Builder, your audit evidence exists the moment an auditor asks for it. DefectDojo Pro adds a dedicated audit log API for instance-wide traceability.

Can DefectDojo enforce our remediation SLAs?

Yes. SLA configurations define how many days your team has to remediate findings at each severity or risk level, per Product. DefectDojo counts down automatically, flags breaches, sends notifications, and tracks mitigated-within-SLA performance on Pro dashboards.

Can I run DefectDojo in a regulated or air-gapped environment?

Yes. DefectDojo Pro deploys in the cloud, on-premises, or in fully air-gapped environments, with SSO via SAML 2.0 and OIDC, and granular role-based access control for enterprise environments.

Is there a free version?

Yes. Community Edition is free, self-hosted, and available under an OSI license, including parser support, deduplication, SLA configuration, and reporting. DefectDojo Pro adds advanced automation, SLA enforcement dashboards, full audit logging, and SLA-backed support.

How is DefectDojo different from a compliance reporting tool?

Compliance reporting tools generate documents. DefectDojo runs your actual AppSec program: aggregation, triage, prioritization, and remediation tracking. The compliance evidence is a natural output of that work, which means it's always current and always defensible.