Security engineers

Security Engineering Without the Busywork

You became a security engineer to find and fix real vulnerabilities. Not copy findings between spreadsheets.

DefectDojo aggregates results from 500+ security tools into one system of action, deduplicates the noise, and automates the triage work that eats your week.

The problem Where the week goes

You're Not Behind.
Your Pipeline Is.

The tools multiplied. The team did not. Most security engineers spend more time managing scanner output than managing risk.

Every Scanner Speaks a Different Language

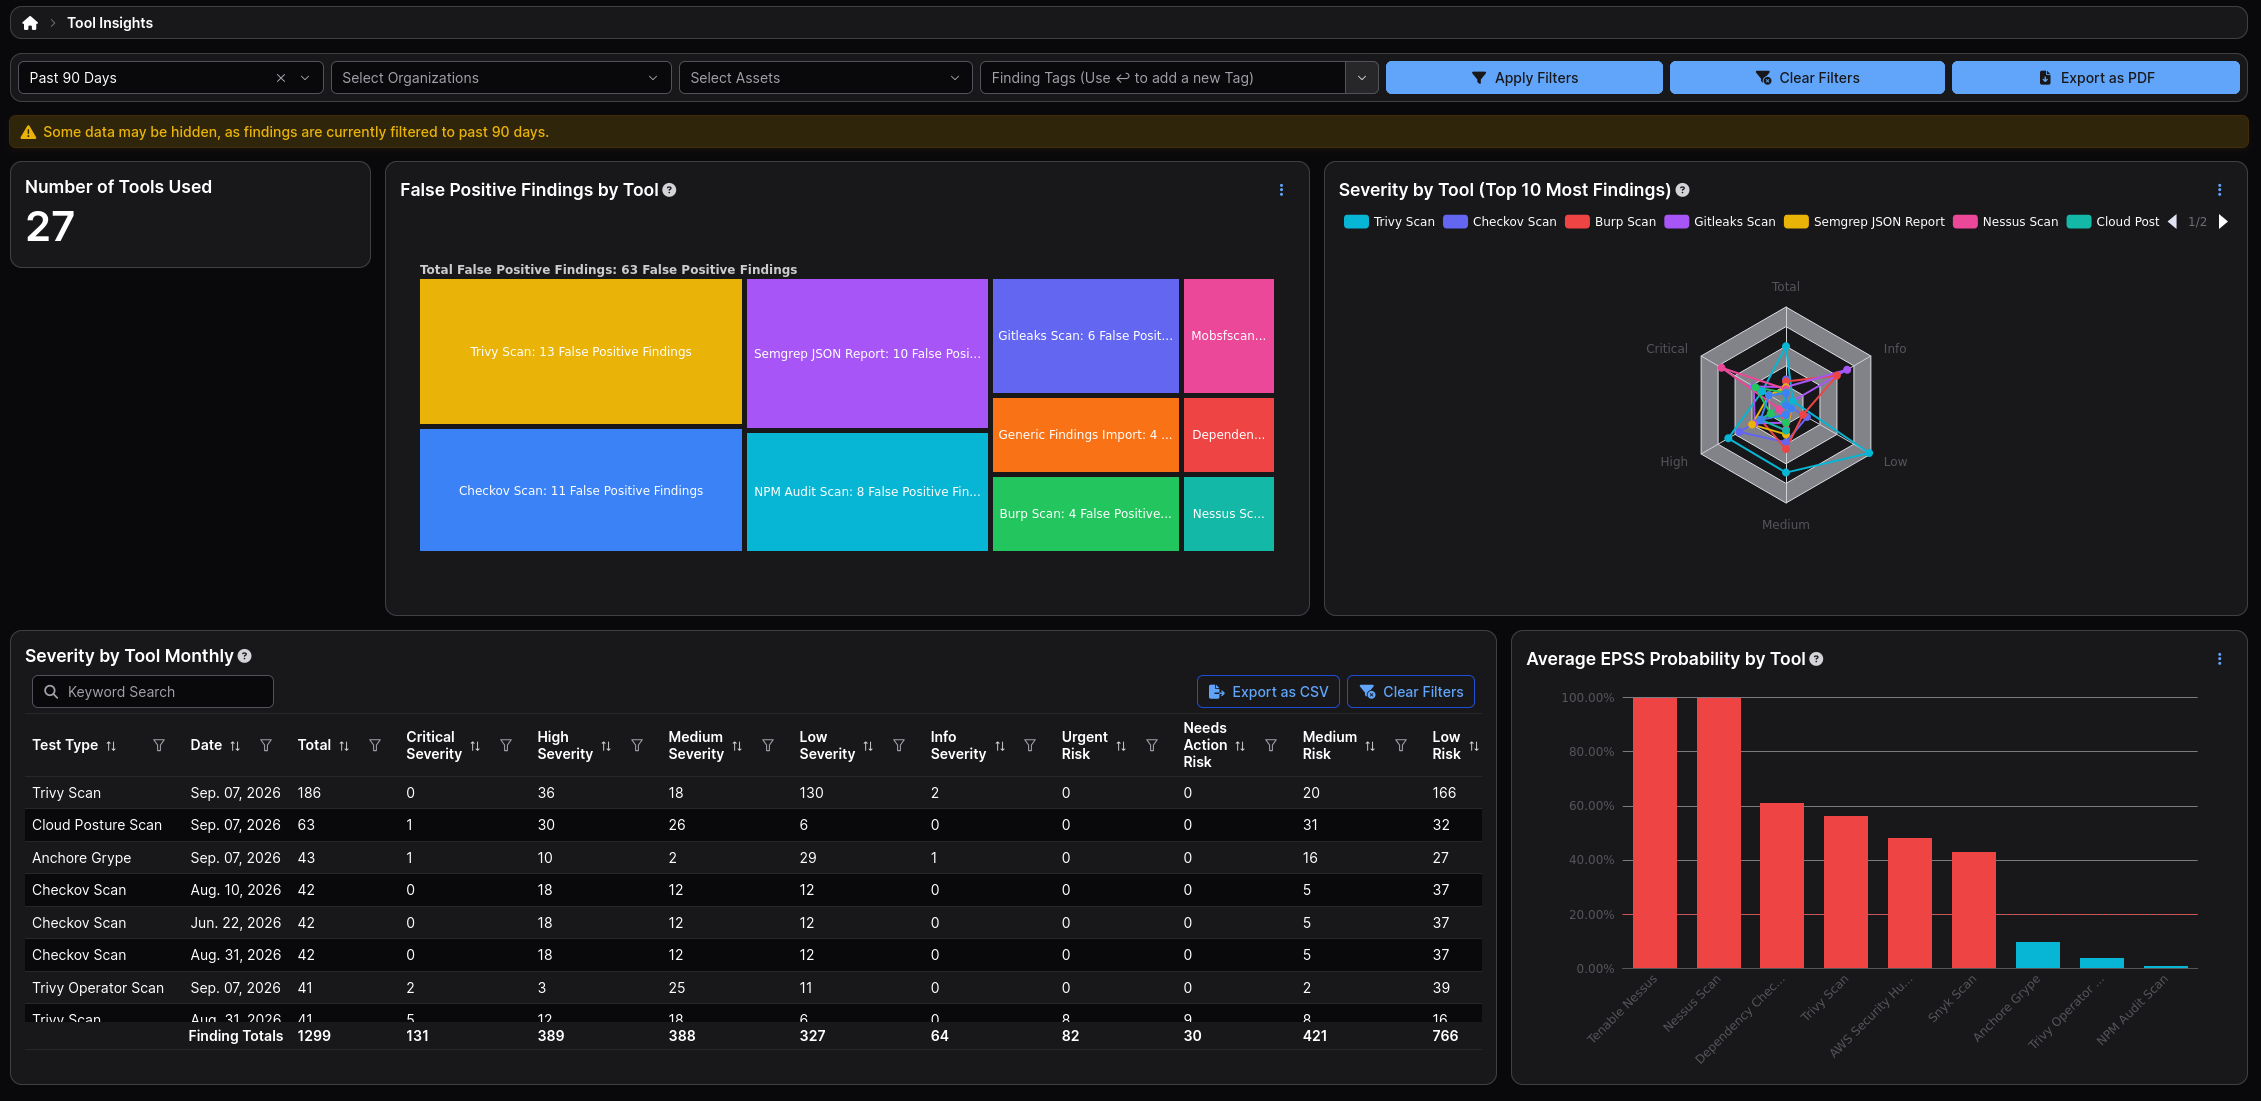
SAST says Critical. SCA says CVSS 9.1. The cloud scanner says High. Your DAST tool has its own scale entirely. Before you can prioritize anything, you have to normalize everything, and doing that by hand across five or ten consoles turns a triage session into a data entry shift.
Every Scanner Speaks a Different Language

Duplicate Findings Bury the Real Ones

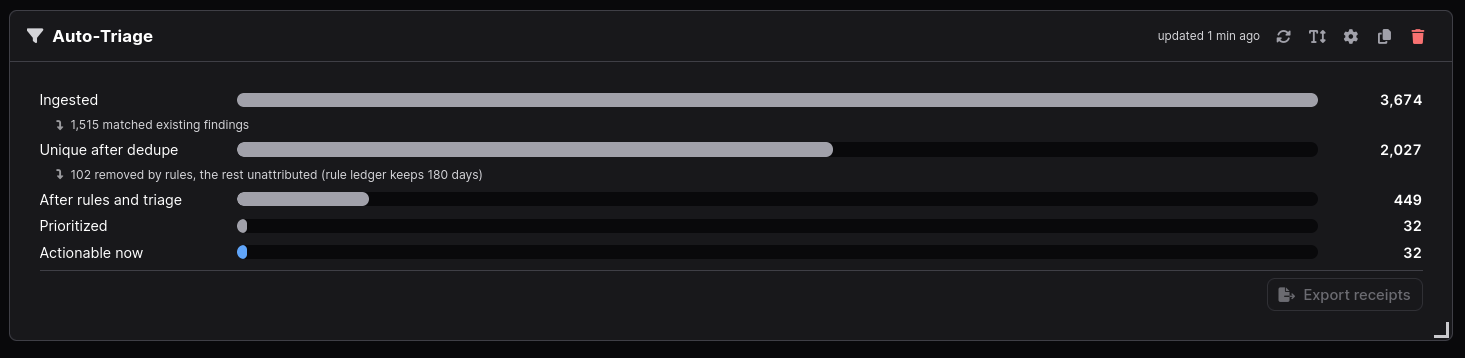
The same vulnerability shows up in every scan, on every branch, from every overlapping tool. Without deduplication, a single flaw can generate dozens of tickets, and the finding that actually matters is somewhere underneath them. Alert fatigue is not a personal failing. It is a pipeline design flaw.
Duplicate Findings Bury the Real Ones

Triage Does Not Scale by Headcount

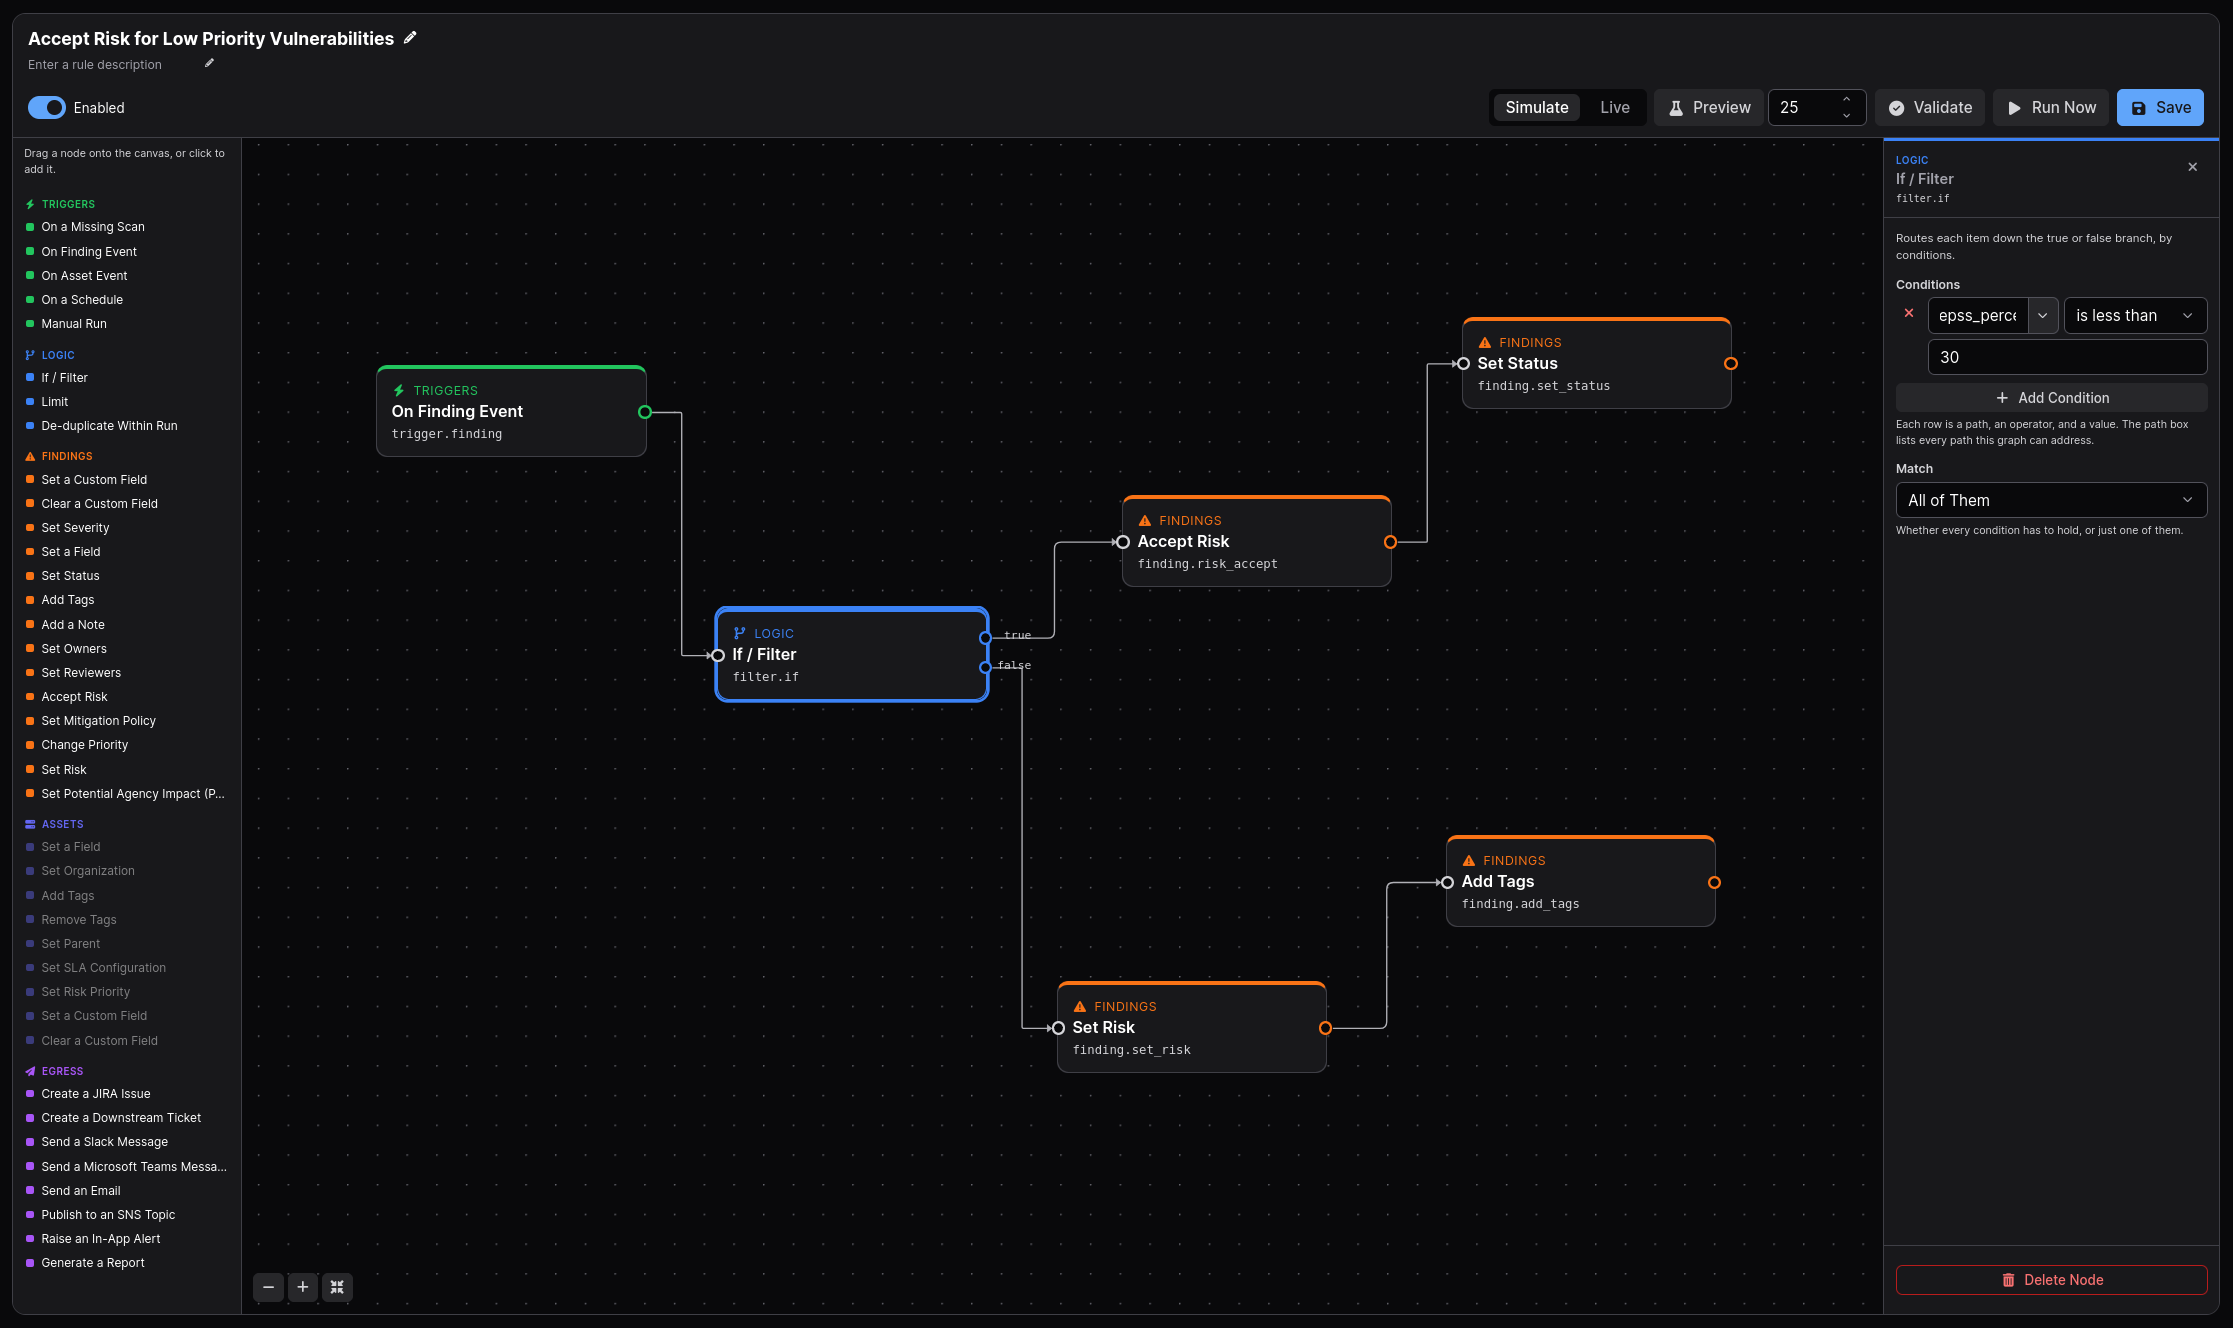
Development ships faster every quarter. Scanners run on every commit. But triage still happens one finding at a time, by a security engineer reading output and making a call. When finding volume grows faster than the team, the backlog becomes permanent and SLAs become fiction.
Triage Does Not Scale by Headcount

Remediation Lives in Someone Else's Backlog

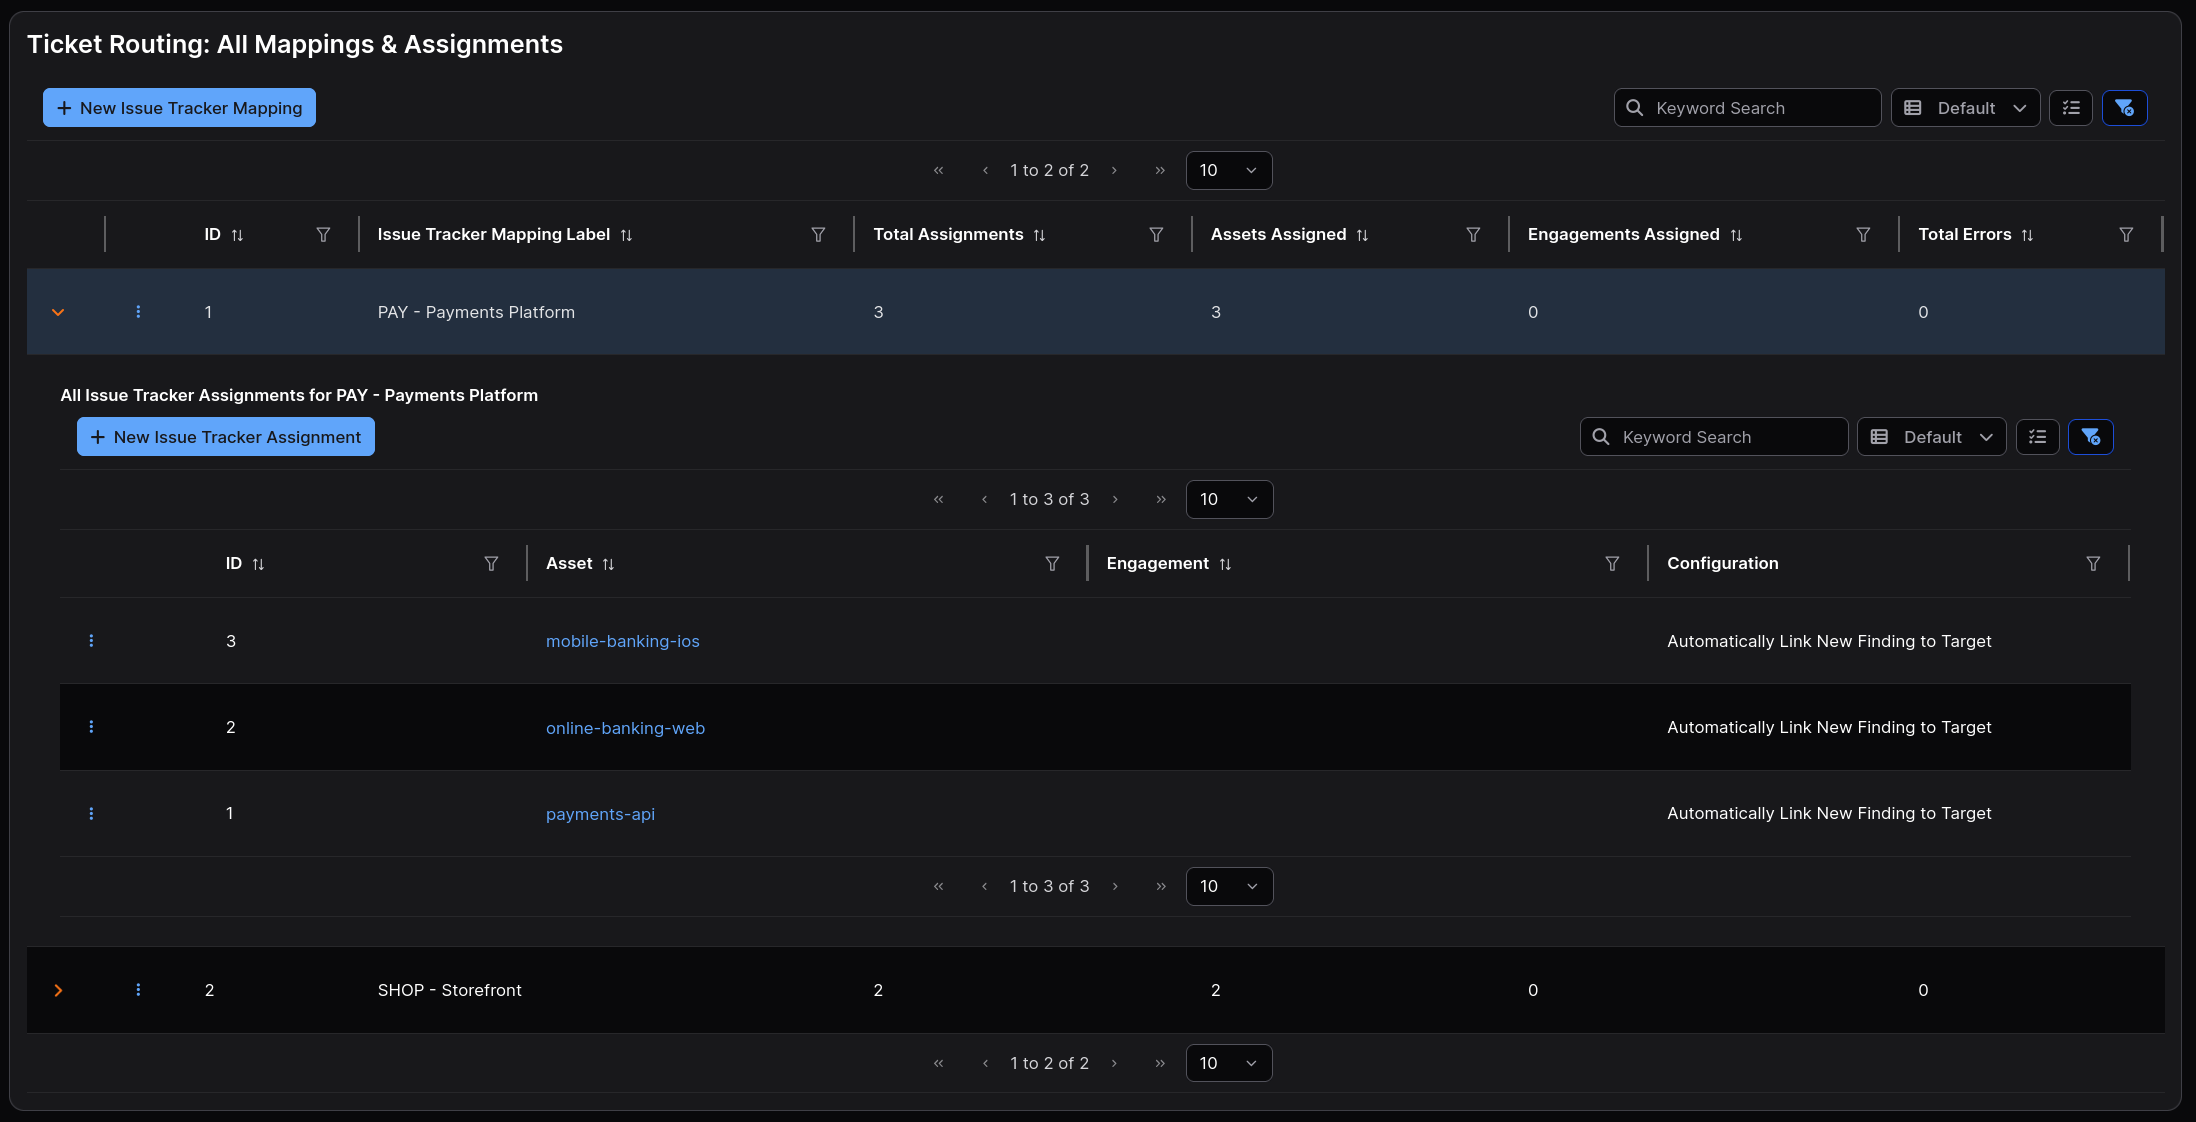
Finding a vulnerability is your job. Fixing it belongs to a developer who works in Jira, not in your scanner console. Every handoff that requires manual ticket creation, status chasing, and re-verification is a handoff that slips. Findings reopen, age out, or quietly disappear until an auditor or an attacker finds them again.
Remediation Lives in Someone Else's Backlog

Proving the Work Is Its Own Job

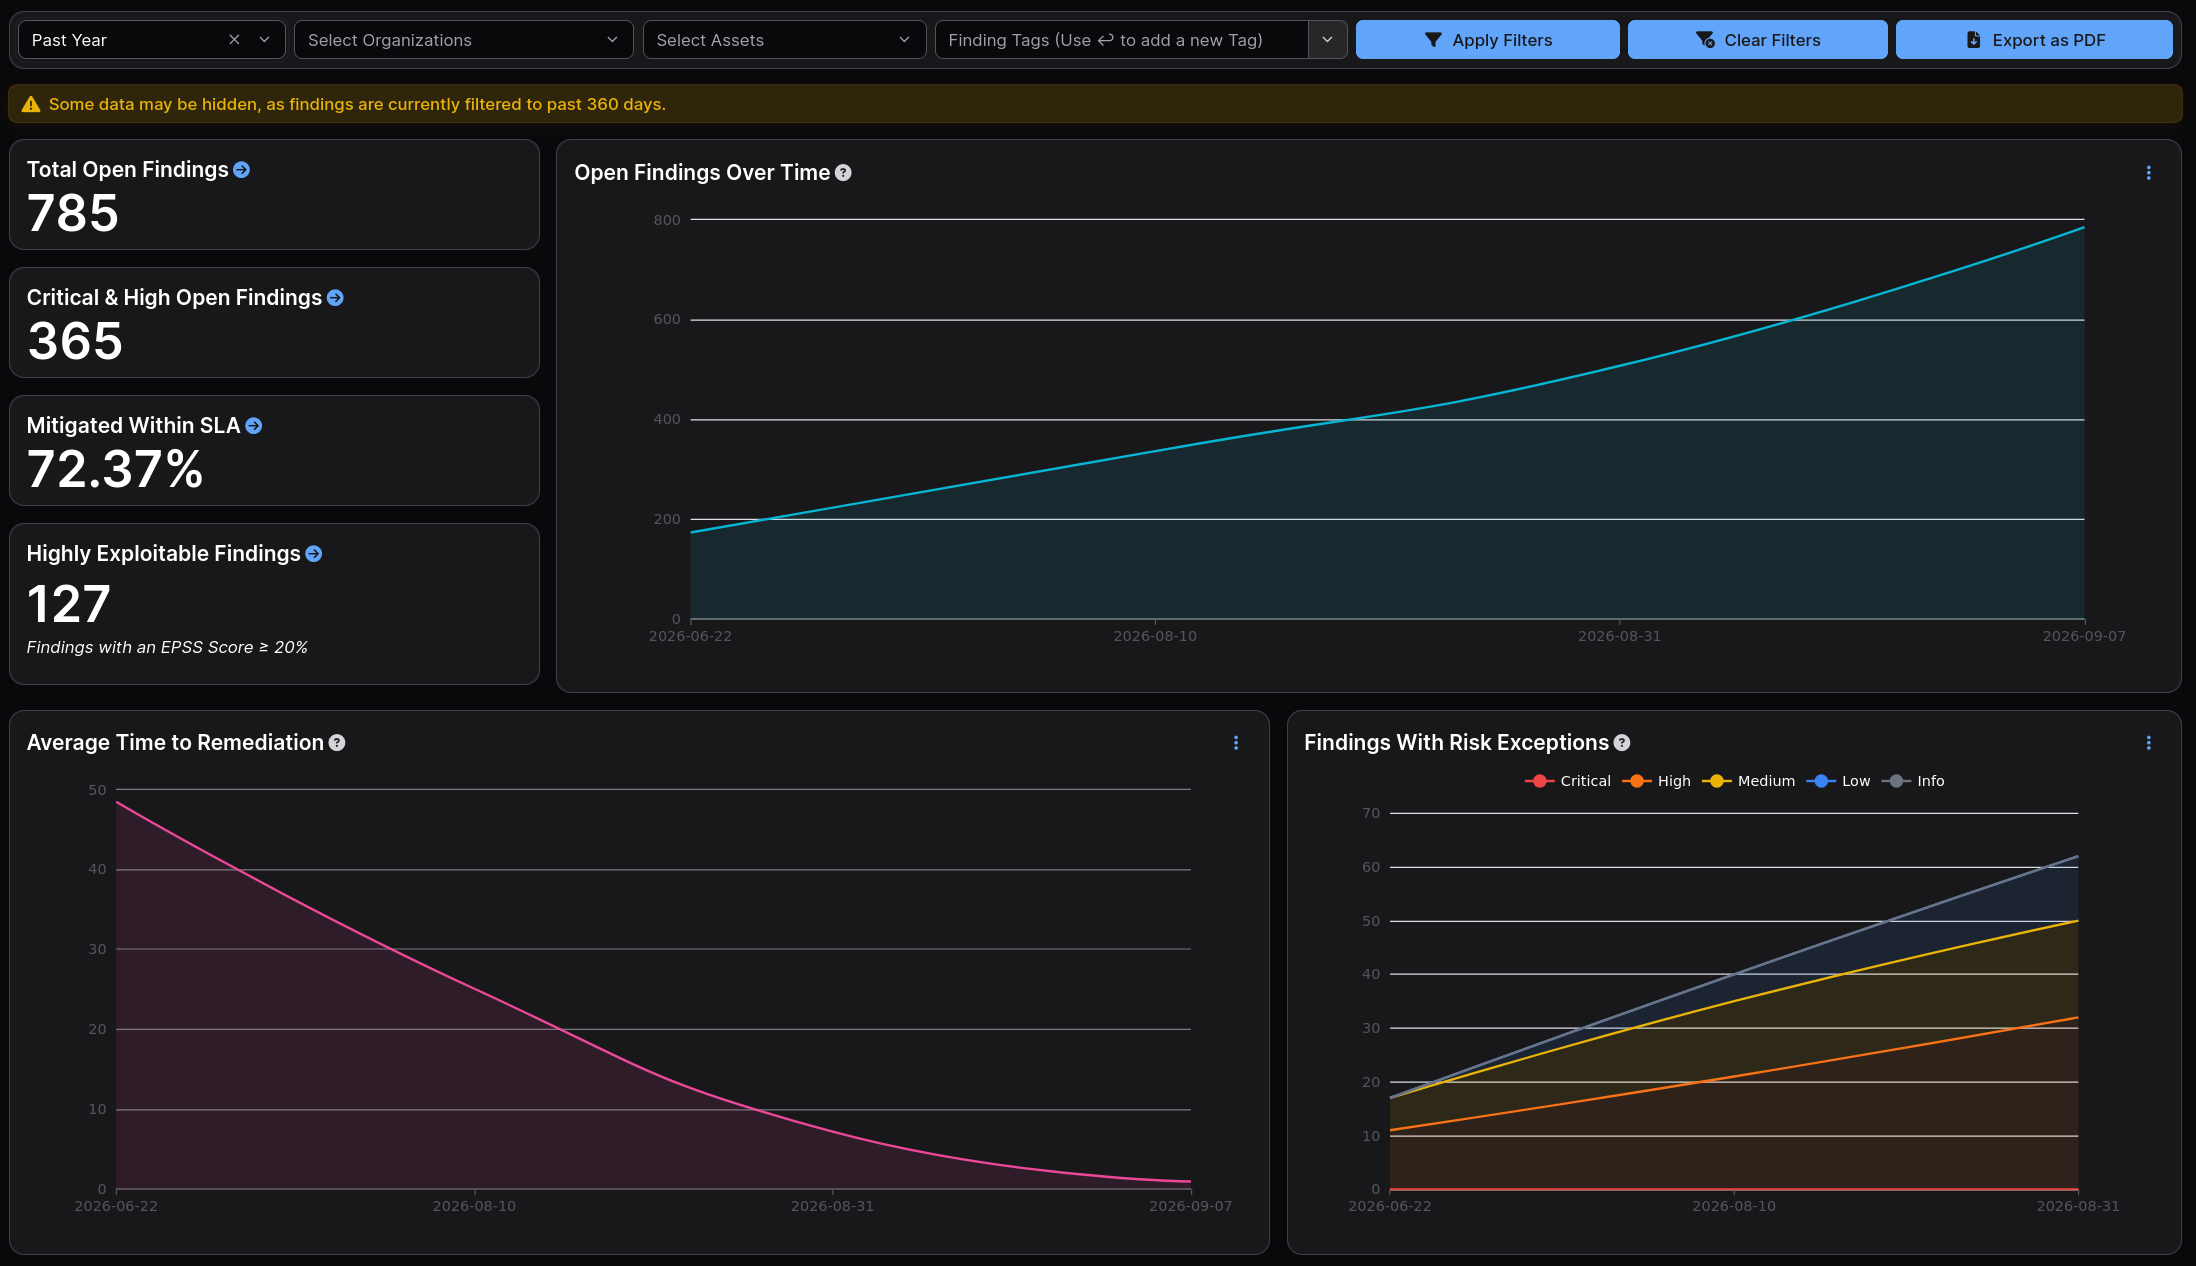
Leadership wants metrics. Auditors want evidence. Developers want to know why this finding and why now. When your data lives in ten disconnected tools, answering any of those questions means hours of manual export and reconciliation, time that comes straight out of actual security engineering.
Proving the Work Is Its Own Job
How DefectDojo helps Aggregate / Prioritize / Fix

How DefectDojo Helps Security Engineers

DefectDojo automates the repetitive layer of security engineering so practitioners can spend their time on judgment calls, not data wrangling.

Aggregate Findings From 500+ Security Tools

DefectDojo's parser library ingests output from more than 500 security tools, normalizing every finding into a consistent format with unified severity. Add a new scanner to your stack and it plugs into the same workflow as everything else. No custom scripts, no format wrangling, no new console to check.

Deduplicate Automatically, Across Scans and Tools

DefectDojo's deduplication engine identifies repeat findings using configurable algorithms, from scanner-provided unique IDs to field-based hash matching. Consecutive scans of the same asset do not create new noise, and reimport handles CI/CD pipeline output without inflating your backlog. You triage each real vulnerability once.

Automate Triage and Enforce SLAs

Set SLA policies by severity and let DefectDojo track every finding against its remediation deadline, with alerting when dates slip. Triage decisions persist: a finding marked as a false positive stays marked across reimports, so you never re-litigate the same call. Rules-based automation handles the routine dispositions so engineers only touch the findings that need a human.

Push Remediation Into Developer Workflows

Bidirectional Jira integration turns findings into tickets in the backlog developers already work from, and syncs status back to DefectDojo when fixes land. Findings retain discovery date, last seen date, and days open across every rescan, so aging data stays accurate and re-verification happens automatically on the next import.

Report Without the Spreadsheet Ritual

Because every finding from every tool lives in one system of action, metrics are a query, not a project. Generate reports on open findings, SLA compliance, remediation velocity, and security posture across your full stack, whether the audience is your team lead, an auditor, or the board.

Start Free, Scale When Ready

Community Edition is free, self-hosted, and born from the OWASP community. DefectDojo Pro adds enterprise scale, advanced deduplication tuning, rules-based automation, and deployment in the cloud, on-premises, or in air-gapped environments. Same platform, same workflow, at every stage of your program.

// Customer proof10,000+ organizations
DefectDojo helped me quickly create a baseline of all vulnerabilities across our entire landscape and build out our risk profile.
Security Engineer

Frequently Asked Questions

What does DefectDojo do for security engineers?

DefectDojo is the open-source unified vulnerability management platform. For security engineers, it aggregates findings from more than 500 security tools into a single system of action, automatically deduplicates and normalizes them, and automates triage, SLA enforcement, and remediation handoffs so engineers spend their time fixing vulnerabilities instead of managing scanner output.

Which security tools does DefectDojo integrate with?

DefectDojo supports more than 500 security tools through its parser library, spanning SAST, DAST, SCA, container scanning, cloud security, infrastructure scanning, and pen test reporting. Popular integrations include Semgrep, Snyk, Burp Suite, Checkmarx, Wiz, CrowdStrike, and Trivy, alongside bidirectional Jira integration for remediation workflows.

How does DefectDojo reduce duplicate findings?

DefectDojo deduplicates findings using configurable algorithms, including scanner-provided unique IDs, field-based hash matching, or a combination of both, selectable per parser. Reimport functionality handles recurring CI/CD scans without creating duplicate finding objects, so consecutive pipeline runs never inflate the backlog.

Is DefectDojo good for product security teams?

Yes. Product security teams use DefectDojo to manage vulnerabilities across an entire product portfolio from one platform. Findings from every tool and every product roll up into a single system of record with consistent severity, SLA tracking, and reporting, which makes cross-product prioritization and posture reporting practical at scale.

Is there a free version of DefectDojo?

Yes. DefectDojo Community Edition is free, self-hosted, and available under an OSI license. It was born from the OWASP community and includes parser support, deduplication, SLA tracking, and the REST API. DefectDojo Pro adds enterprise features and deploys in the cloud, on-premises, or in air-gapped environments.