CISO and AppSec leaders

You are accountable for a number you cannot produce.

One defensible view of risk, across every business unit and scanner.

Your board wants answers, not scanner exports. DefectDojo unifies findings from 500+ security tools into a single system of action, so CISOs and AppSec leaders can measure risk, prove progress, and report on security posture with confidence.

The problemReduce risk and prove it

The Biggest Challenges Facing Security Leadership

Every CISO owns the same mandate: reduce risk and prove it. Most inherit a tool stack that makes both nearly impossible.

You Can't Report on What You Can't See

Every scanner in your stack tells a different story in a different format. SAST, DAST, SCA, cloud, and pen test results live in separate consoles with separate severity scales. When the board asks "are we getting better?", stitching the answer together by hand takes your team days and the numbers still don't reconcile.
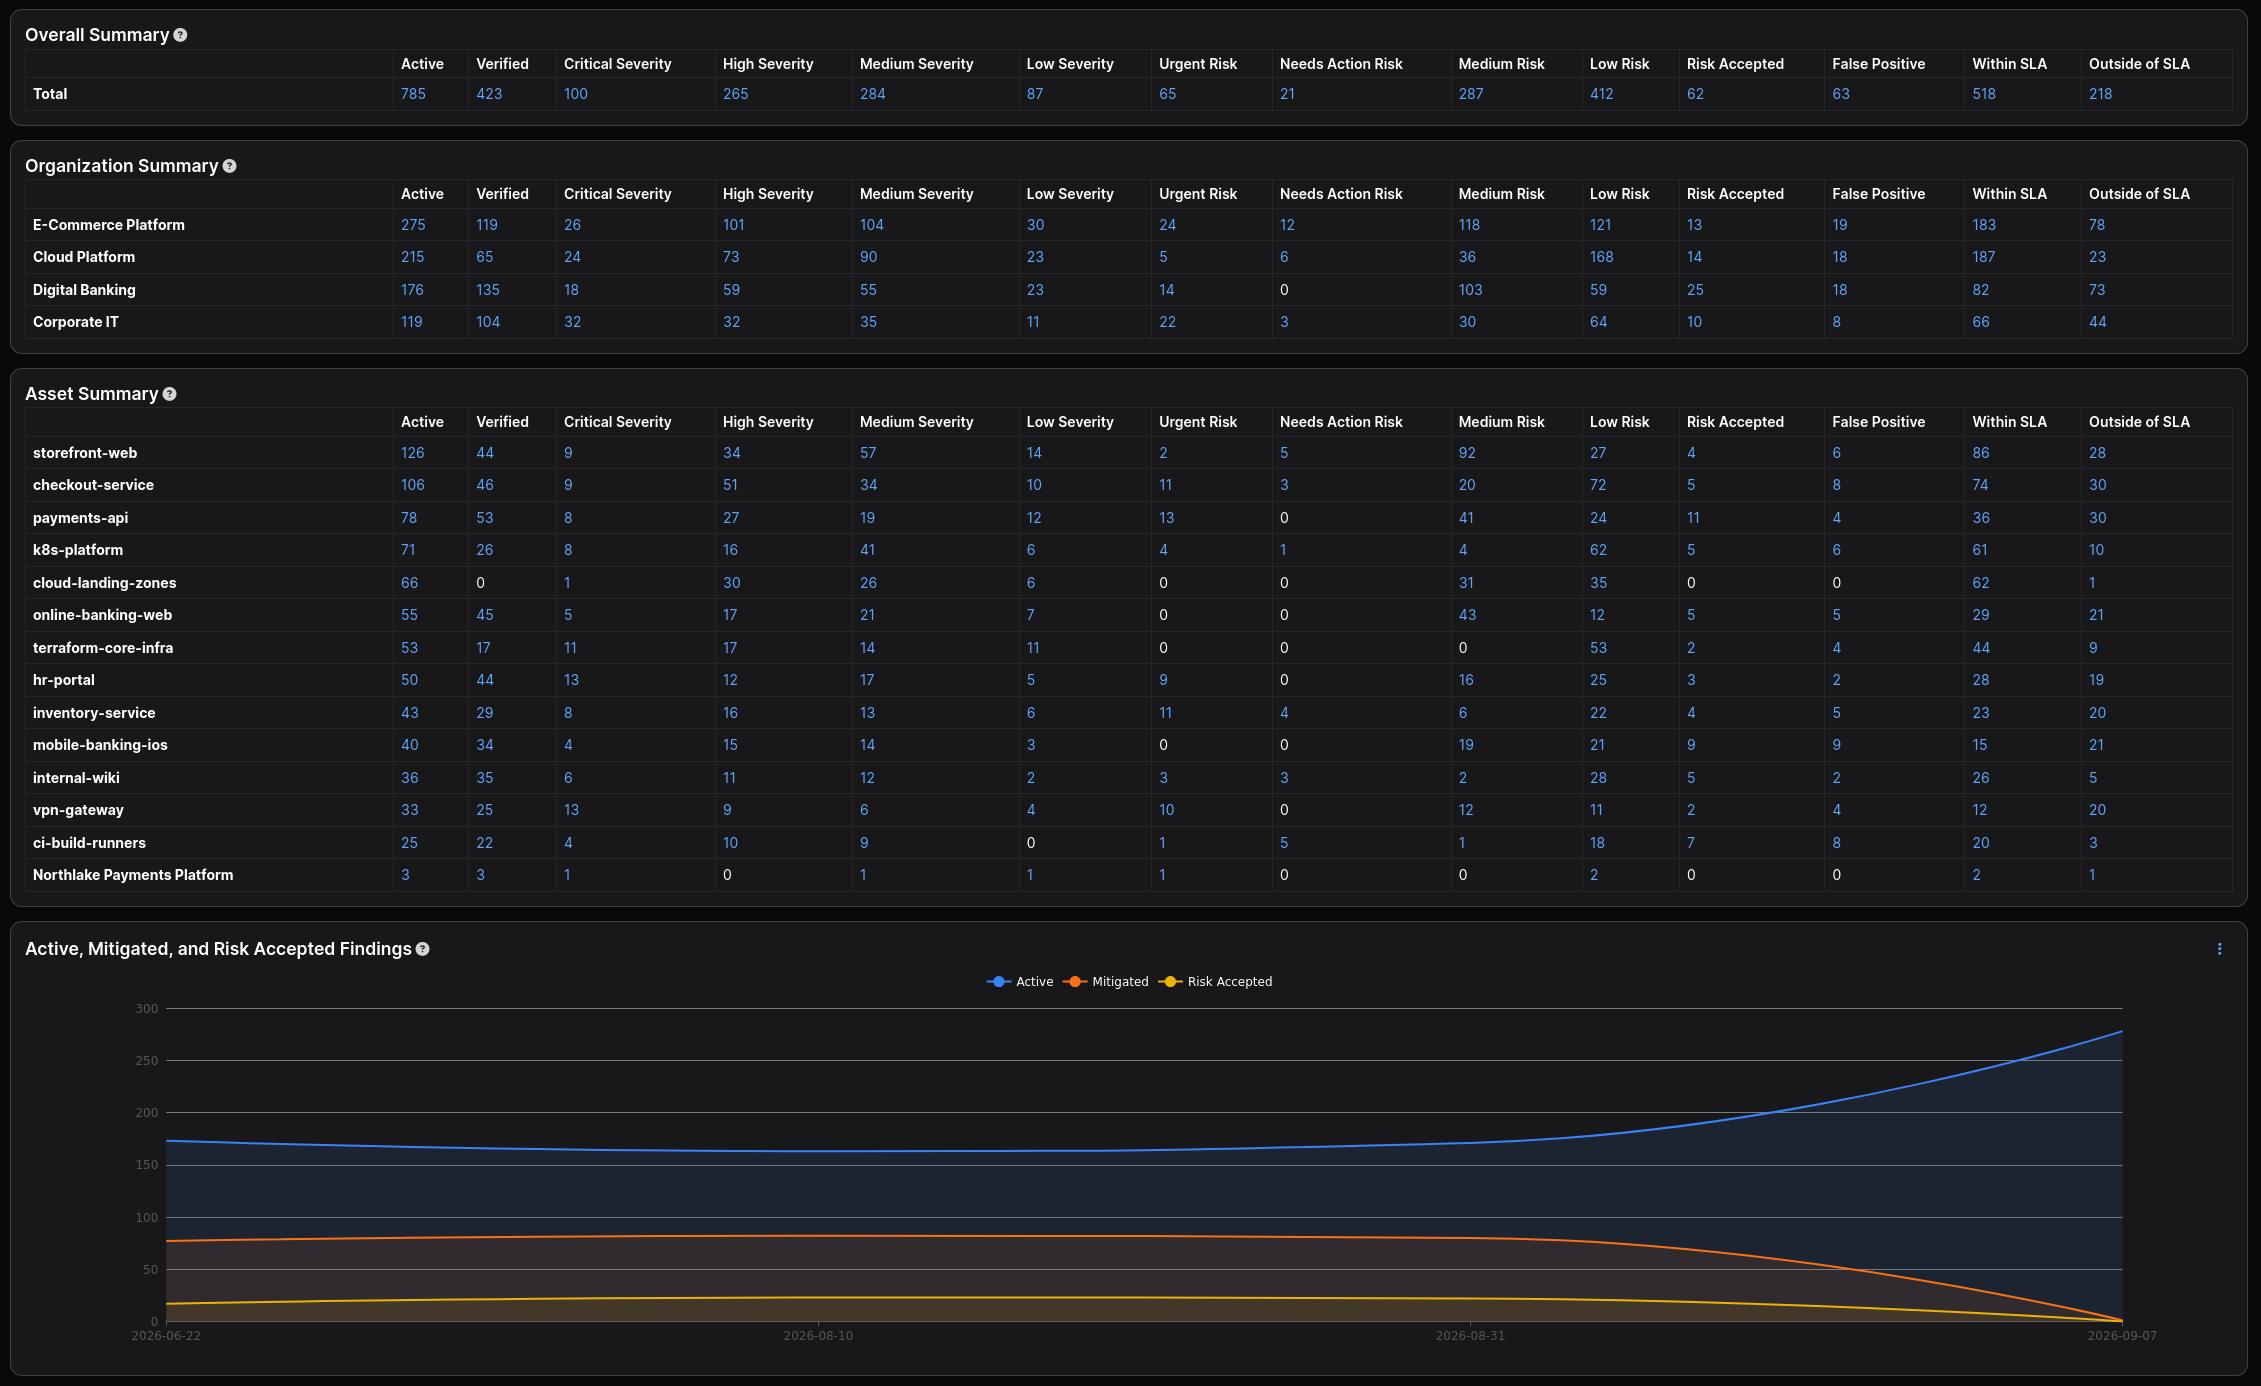
You Can't Report on What You Can't See

Your Team is Drowning in Noise. Not Managing Risk

Duplicate findings, false positives, and untriaged backlogs consume the hours your AppSec team should spend on real risk. Headcount is flat, scan volume is not. Without automation, security leadership is forced to choose between coverage and sanity.
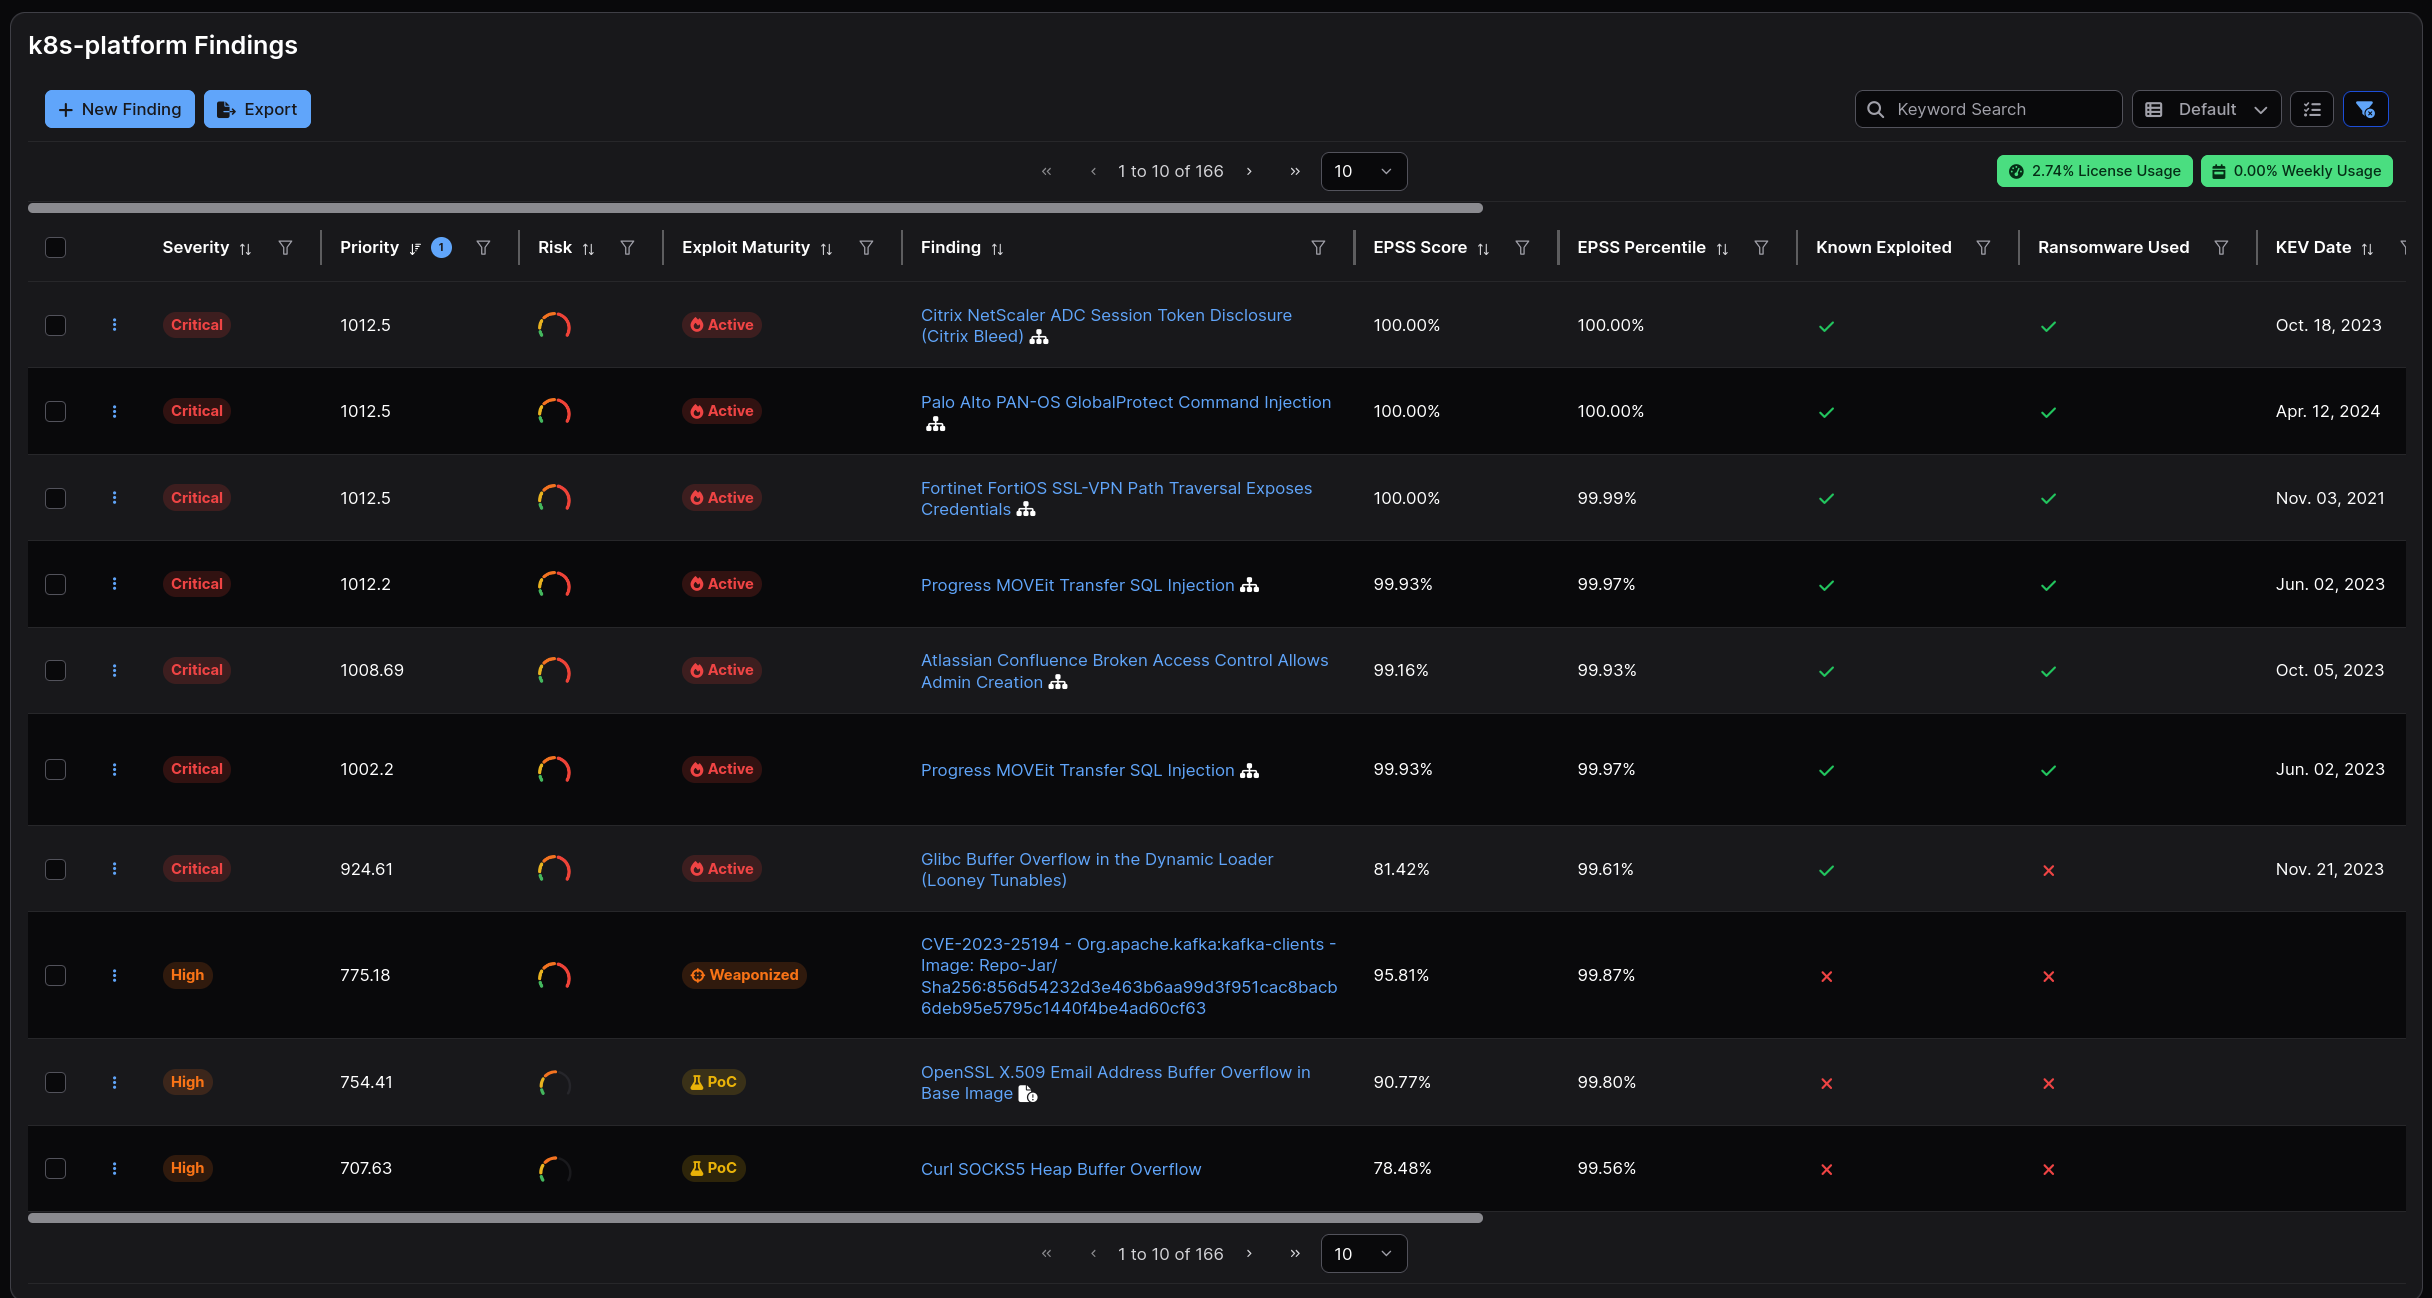
Your Team is Drowning in Noise. Not Managing Risk

Compliance Is a Fire Drill Instead of a Byproduct

SOC 2, PCI-DSS, and the EU Cyber Resilience Act all demand evidence that vulnerabilities are tracked, prioritized, and remediated within defined timelines. When that evidence is scattered across ten tools and a spreadsheet, every audit becomes a scramble and every attestation carries risk.
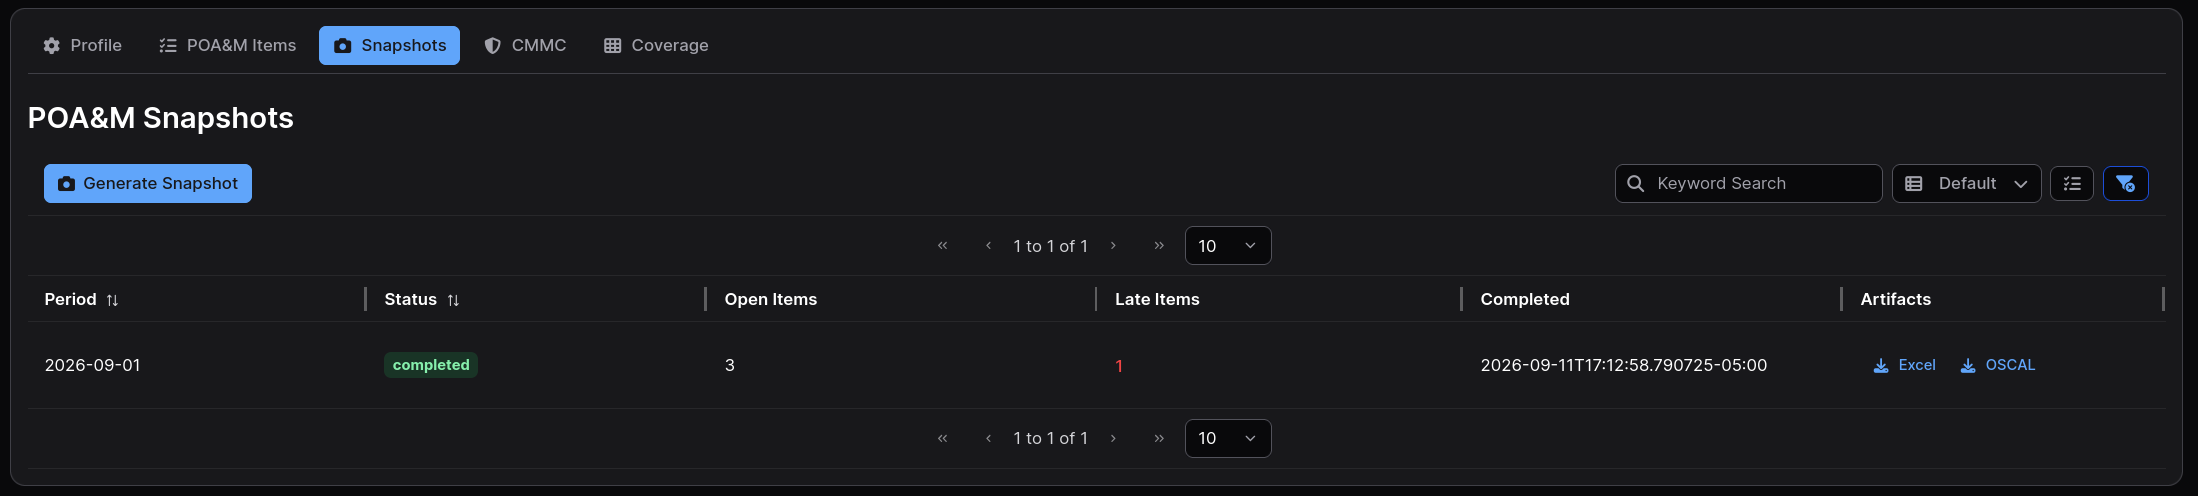
Compliance Is a Fire Drill Instead of a Byproduct

Tool Spend Keeps Growing, Outcomes Don't

Security budgets get scrutinized in every planning cycle. Without data on which scanners actually surface actionable findings, CISOs can't defend spend, consolidate the stack, or negotiate renewals from a position of strength.
Tool Spend Keeps Growing, Outcomes Don't
How DefectDojo helps Aggregate / Prioritize / Fix

How DefectDojo Helps CISOs and AppSec Leaders

Every finding from every tool lands in one data model, deduplicated and ranked by real exploitability. The number is always current, and you can defend how it was calculated.

DefectDojo turns fragmented scanner output into the metrics, evidence, and accountability that security leadership needs.

One System of Action for Your Entire Security Program

DefectDojo aggregates findings from more than 500 security tools into a single pane of glass, then automatically deduplicates, enriches, and prioritizes them. Every finding, every asset, every remediation lives in one place, giving the CISO a defensible, complete picture of security posture.

Board-Ready Reporting Without the Manual Work

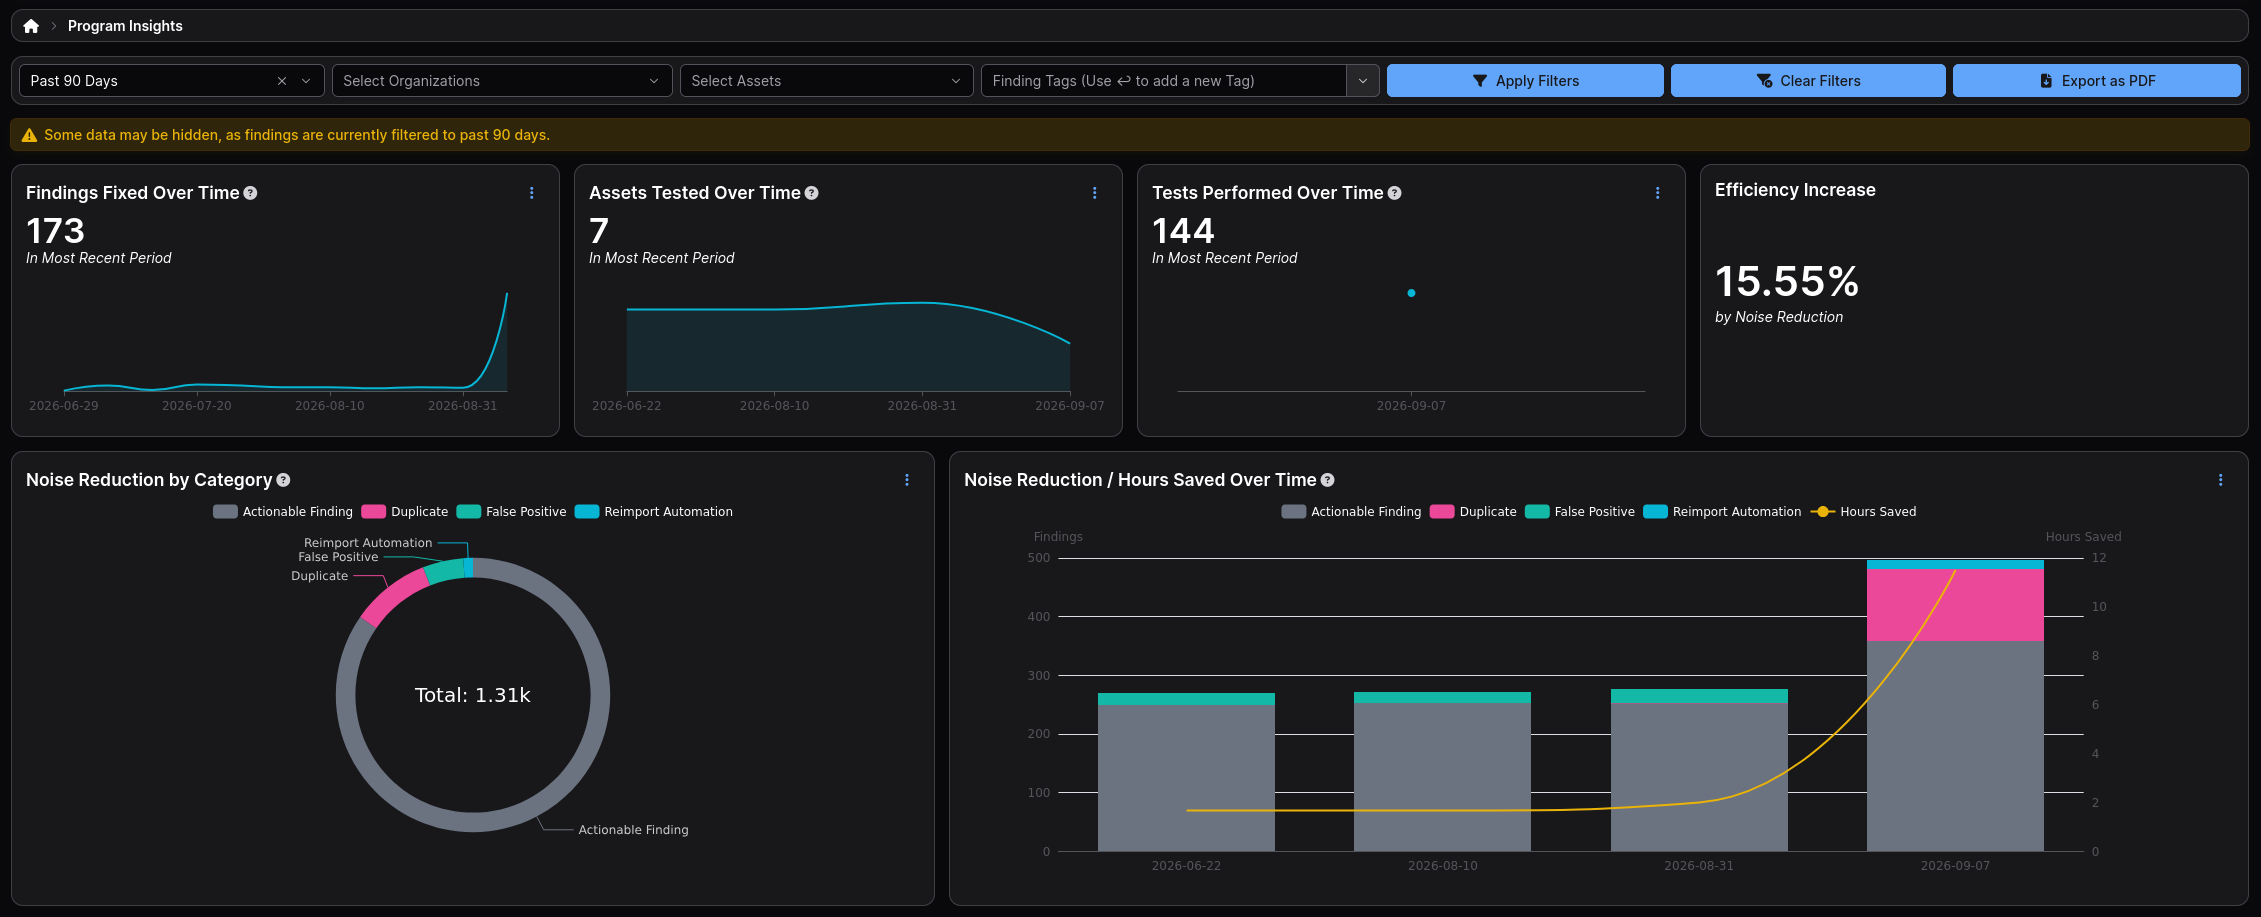
DefectDojo Pro's dashboards are built for stakeholders at every level. Whether you're looking for overall program-level posture or measuring how effective your different scanners are, there's a view that answers the question and a custom report builder to put it in front of the people who need it.

Risk-Based Prioritization Your Team Can Defend

DefectDojo enriches findings with daily-updated EPSS exploitability data, so your AppSec team works the vulnerabilities most likely to be exploited instead of chasing raw severity counts. When leadership asks why something was deprioritized, the answer is data, not opinion.

SLAs That Turn Policy Into Accountability

Define remediation SLAs by severity, track them automatically, and report on compliance across the portfolio. SLA performance becomes a metric you manage, not a promise you hope holds up in an audit.

Compliance and Audit Readiness as a Byproduct

Because every finding and remediation is tracked in one system, evidence for SOC 2, PCI-DSS, and the EU Cyber Resilience Act is already assembled when the auditor arrives. Reporting on compliance posture becomes routine instead of a quarterly fire drill.

Prove and Optimize Your Tool Spend

Tool Insights shows which scanners produce actionable findings and which produce noise, based on the count and severity of what each tool reports. Add tools, compare results, or swap vendors with no program impact, and walk into renewal negotiations with evidence.

// Customer proof10,000+ organizations
DefectDojo turned security from a spreadsheet problem into a solved problem.
CISO

Frequently asked questions

How does DefectDojo help CISOs report to the board?

DefectDojo Pro includes an Executive Insights dashboard that summarizes the current state of your security program, plus filterable metrics for remediation performance, team effectiveness, and tool performance. Any dashboard view can be exported as a PDF, and the Report Builder produces reusable, polished reports with executive summaries for recurring board and leadership reporting.

Can DefectDojo replace our spreadsheet-based vulnerability tracking?

Yes. DefectDojo is a unified vulnerability management platform that aggregates findings from more than 500 security tools, deduplicates them automatically, and tracks every finding through triage, prioritization, and remediation. It serves as the single system of action that spreadsheets were never designed to be.

How does DefectDojo support compliance reporting?

DefectDojo tracks every finding, SLA, and remediation in one auditable system, so security teams can report on posture and compliance across frameworks including SOC 2, PCI-DSS, and the EU Cyber Resilience Act. SLA configurations appear directly in report executive summaries, giving auditors the evidence they need without manual assembly.

What security tools does DefectDojo integrate with?

DefectDojo aggregates findings from more than 500 security tools, including SAST, DAST, SCA, container, cloud, and infrastructure scanners, as well as pen test results. Findings can be pushed to Jira, GitHub Issues, and other trackers to route remediation to the teams that own it.

Is there a free version of DefectDojo?

Yes. DefectDojo Community Edition is free and available under an OSI license, born from the OWASP community. Organizations that need advanced dashboards, the Report Builder, and enterprise support deploy DefectDojo Pro in the cloud, on-premises, or in air-gapped environments.